General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! Total number of profiles (101) exceeds platform capacity (100)

Hello all, I have a PA-820 and I am experiencing the same issue described here:https://live.paloaltonetworks.com/t5/general-topics/total-number-of-profiles-xx-exceeds-platform-capacity-xx/td-p/243231 My current configuration includes the following: 208 security rules.35 nat Policy rules3 QOS Policy rules24 decryption Policy rules5 Application Ov...
mrjcap by • L1 Bithead
  • 7058 Views
  • 2 replies
  • 0 Likes

Traffic Logging for Path Monitoring

I'm wondering if the Palo Alto firewall (PA3020) logs the ping traffic of a path monitoring setup, or if it can be configured to do so.Let me explain why.We have configured path monitoring on the default route through our primary ISP. During manual testing (unplug the ethernet cable) the failover to the secondary works just fine. However, we'v...

Resolved! Change device group tree

Hello,Now my Panorama managing 4 cluster, 3 in Emea and 1 in US.This the Device Group organization. Shared Cluster 1 Cluster 2 Cluster 3 Cluster 4 Now we want to modify the organization to split the Emea Cluster and US Cluster: SharedEmea:Cluster1cluster2cluster3US:Cluster1Should be easy like that:Create 2 new empty Device Gruop...

Resolved! Customer Support Account Without Device

Hello, We would like to transfer management of a customer's device from our support account, to theirs. However, they do not currently have a customer support account. All the documentation I have read online indicates that you must register a device in order to create a customer support account. As we currently manage the device, there is no de...

datapalne issue

I have 2 Paloalto firewalls working as ha active-passive, yesterday we had HA test so try to pass the traffic to the passive device buy suspend the active, the passive become active everything works fine till now my issue is the interface of the firewall 2 is not responding to anything ping or anything my network is down in Cisco switches showin...

Automate traffic log export to csv

Hi all,I need to automate the export to csv for a specific query for traffic log, for example (zone.src eq myzone) and (time_generated in last-calendar-day) and I must have the same fields extracted from the gui, without limit to the rows retrieved. I've tried to:- export the command from cli to csv -> nothing useful- create a custom report -...

N2Z2 by • L2 Linker
  • 2939 Views
  • 2 replies
  • 0 Likes

Thank You for Filling Out the LIVEcommunity Experience Survey!

If you've visited LIVEcommunity anytime recently, you've probably seen a pop-up asking for your feedback. We've deployed this survey since April 2020 for new and returning visitors alike as a way to gather feedback from our users. In the past six months, we've had more than 600 responses to this survey! But no amount of feedback is too much. ...

survey-livecommunity.png
jforsythe by • Community Team Member
  • 27650 Views
  • 1 replies
  • 4 Likes

Global Protect users unable to access internal resources

I have a new portal and gateway and I'm trying to get users to access internal resources. I can see connections in the monitoring logs and get session end reason of either aged-out or n/a. Internal resources are able to reach GP users so the traffic is flowing outbound correctly. Somewhat new to PA and I'm thinking I'm missing a route or a NA...

Resolved! Dual ISP and PBF

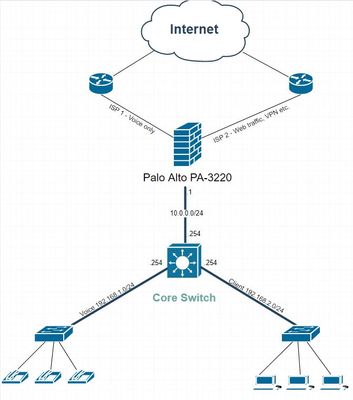
Hi, currently we have one ISP and our interVLAN routing between internal networks is done by the core switch. In the future we plan on obtaining a second WAN connection which is to be used exclusively for voice traffic. Every other type of traffic should use the other WAN connection. Can this be achieved with PBF? If so, what is best practice f...

Topology.JPG

log forwarding

Team, Have few questions on log forwarding .. 1. Is there any best option to check what are the policy rules doesn't configured with log forwarding from Panoroma or any other tools ? 2.How to enforce users to specific custom log forwarding profile 3. is there any alert system we can configure if user configure policy without log forwarding pro...

Initial GlobalProtect connection and subsequent drop-outs.

It routinely takes me over 10 minutes to login to my VPN every morning, because the network response is so slow and droppy. There's so much already loading when I login that I receive "cannot connect" errors from other apps before GlobalProtect even prompts me. I have gigabit Internet at home with speeds routinely registering at over 300mbps, ...

z-anon by • L0 Member
  • 2299 Views
  • 1 replies
  • 0 Likes

Rule creation query

Hi Team, We have created policy Source: Internal subnetDestination: Any Application:Any service/url category:custom category.Action allow. In custom URl category, we have added 2 domains. Our requirement is internal subnet user should access these 2 domains only.However traffic is getting allowed for all other destination IP address. Why it is h...

BNSRIKAR by • L1 Bithead
  • 2347 Views
  • 2 replies
  • 0 Likes

Validation failed when committing a changes to managed firewalls from Panorama

Last week we made a changes(added new IP addresses as a Source) to the existing security policy and tried verifying by validating template/device group for target firewalls however it results in validation failed with following errors. user-id-agent unexpected hereVsys is invalidDevice is invalidConfiguration is invalid Any help and suggestions...

Globalprotect dissonnection issues

I have a couple of users who say that when on the GP VPN client it disconnects them multiple times and I have not been able to reproduce their issues.The only thing I have found so far is this in the system logs "globalprotect gateway user login failed. error existing user session found" collected logs on the client and nothing really stands out...

jdprovine by • L4 Transporter
  • 28293 Views
  • 43 replies
  • 0 Likes
  • 24479 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





