General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

VPN Tunnel IPSEC L2L VPN NAT not acting as intended

I am Labbing up a configuration I am about to go live with in production but it is not acting as it should when trying to apply a NAT rule to a tunnel interface. When I apply individual rules to the vpn traffic as I would like it to act I am not getting the intended result. I have to select bi-direction to get the NAT rule to act as it should. I...
alliman by • L0 Member
  • 2629 Views
  • 1 replies
  • 0 Likes

Resolved! Palo Alto Terminal Server Agent - How to monitor Citrix non-persistent virtual desktops

Hello, In our Citrix Virtual Apps and Desktops environment (On-prem 2106) we are only able to monitor user info from the XenApp servers where users launch a published application. Is it possible to monitor user info from non-persistent Windows 10 virtual desktops? Each desktop has its own IP address. Thanks!

Appid ms-teams-audio-video vs ms-lync-audio

We're having both legacy lync users and Teams users in our network. But for the life of me: I don't seem to get hits on "ms-teams-audio-video" .Is it because the data itself is not different enough so the contentid engine can't see the difference? Does it need decrypting to see the difference? Using the latest appid updates on a PANOS 9.1 If any...

KenVaBr by • L1 Bithead
  • 3129 Views
  • 1 replies
  • 0 Likes

Resolved! Log viewer not working for 8.1.13 PAN-OS

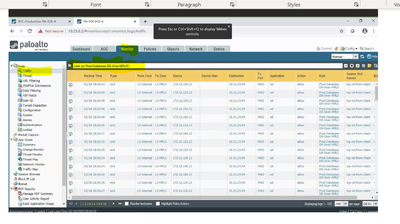
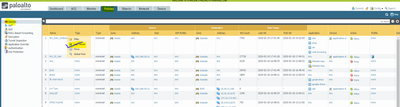
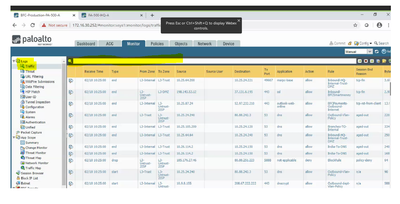
Cx facing this issue with PAN-OS 8.1.13 . From the policies tab when we are selecting log viewer option for any security policies rule then it redirected to the Monitor tab . Logs traffic tab there it is showing all firewall traffic and filter bar tab we could not able to see any filter.But another PAN-OS version we already checked we have found...

Sonu_Singh_0-1582119899809.png
Sonu_Singh_1-1582120233668.png
Sonu_Singh_2-1582120793761.png
bit_byte by • L2 Linker
  • 20422 Views
  • 16 replies
  • 1 Likes

Missing Secure Flag on the SSL Cookie after a vulnerability assessment ran on PA820

In my case, the team is performing a vulnerability assessment on PA820Vulnerability Title: Missing Secure Flag From SSL Cookie Description: The Secure attribute tells the browser to only send the cookie if the request is being sent over a secure channel such as HTTPS. This will help protect the cookie from being passed over unencrypted requests....

Barracuda to Palo Conversion

I've tried searching but have not been able to find much information. Does anyone have experience converting a Barracuda ng800 to Palo Alto? I'm working with someone that just received a pair of PA-5200 series firewalls and want to move their Barracuda config over to them.I don't think Barracuda is a supported firewall type in Expedition, but ma...

Resolved! GlobalProtect Certificate to Encrypt and Decrypt Cookies

Hi All,I'd like to find out what type of certificate you need if you are configuring Authentication Override for GlobalProtect Portal and Gateway. That is, for the option to specify a certificate to Encrypt/Decrypt Cookie (screenshot below), does this need a Machine Certificate, Web certificate??? Secondly, what is the behaviour if you don't spe...

override.PNG
Bocsa by • L3 Networker
  • 23800 Views
  • 5 replies
  • 1 Likes

GlobalProtect multiple gateways

Hi All, Similar to a Cisco ASA tunnel-group configuration where we can have different VPN configurations using the same public IP, I wonder if similar configuration can be achived on Palo Alto. My objective would be to configure different gateways using the same public IP address, however i haven't yet grasp how can i specify which gateway to us...

ipsec question

Hello,Do I need a tunnel interface for site to site vpn ? If yes How can I do that and what is the benefit Thanks

tifotano by • L0 Member
  • 2010 Views
  • 1 replies
  • 0 Likes

destination port in PBF

Is there an option to define destination port in PBF. Now if a service is selected, PA applies PBF if source or destination has that port.I am looking for a PBF which should match only if destination port is 80.

ceapen01 by • L2 Linker
  • 2790 Views
  • 3 replies
  • 0 Likes

Dynamic updates not working after RMA replacment - Download Error Problem with local SSL certificate

We recently got a RMA replacement in for a failed PA5250 in HA but we are now noticing that Dynamic updates are not downloading and installing. We get a message in the Panorama Job Schedules section stating "Failed to upload image. Device msg:'Failed to download panup-all-antivirus-3977-4488. Download error:Problem with the local SSL certificate...

cruz77 by • L1 Bithead
  • 2519 Views
  • 1 replies
  • 0 Likes

Resolved! Always on Global Protect

Hello All, Looking to get advice on this topic. The idea is to have the users connect via a VPN tunnel regardless of their location, internal LAN or working from home, etc. I need to make it easy on the users so its to a burden, e.g. having to authenticate to the vpn after logging into heir workstations with similar creds. I'm thinking of someth...

Resolved! How to find a URL for session_end_reason eq decrypt-error

I have SSL Decryption and URL Filtering implemented and I see lots of decrypt-errors listed as session_end_reason. Is there a way to see the exact URL that the user was attempting to connect to? That way I can troubleshoot the site and see if an exclusion is needed. Version 9.1.10

exclude a network from static route

Is it possible to exclude a network from static route. For eg I have static route 10.20.0.0/16 to the core-switch.unfortunately my management network (including PA) is 10.20.200.0/24I dont want traffic to 10.20.200.0/24 going to core switch. just exclude that network from the route. As it's directly connected to PA, it should take that path by ...

ceapen01 by • L2 Linker
  • 4602 Views
  • 3 replies
  • 0 Likes
  • 24479 Posts
  • 125 Subscriptions
Top Solution Authors
Labels