Script to create multiple nodes on PANOS
Hi all, Is there a quick way to script / create 50+ nodes on a PA Firewall (azure based)? Cheers.D
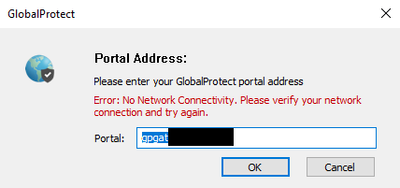
Hi all, I've deployed a GlobalProtect installation solely for the purpose of User-ID. The GP agent connects to the internal portal/GW (one box) upon login with Kerberos SSO. However, when the internal gateway is not reachable (user has no network, user isn't on-prem), the GlobalProtect Agent notifies the user about this (no network / can't reach...
Hello Community, i'm currently planing a project which should be able to control the VPN user access via the API.It should be a simple tool where you just need to click a single button. The tool then activates or deactivates the user for that VPN via the API.How do i activate/deactivate local user on the PA with the API?I've already searched thr...
It is possible to block Personal Gmail, but not business GSuite within Palo?
Hello, I have to do a TCPDUMP to test the communication of my Active Directory because a have a problem with the User-ID service. I have read the documentation and I don't understand when says that the TCPDUMP captures the traffic that traverses the MGT interface. So what happens with the traffic that traverses the data plane and not the manage...
Hi, Let's say a scenario where I have a default route configured to go out interface 2 with a Metric of 10 Then I have another static route to go out interface 3 with metric of 5. On this route I setup path monitoring to ping an ip address that is accessible to both interface 2 and interface 3. Does the static route path monitoring ensure that i...
Is there any timeframe for when the new NCAA app-id's released for March Madness? I found the 2017 app-is signatures, and a link for the 2018 signatures but was not able to access the files.
Running PanOS 8.1.1 & GlobalProtect Agent 5.1.0 & connect method Pre-logon (Always On) When connected and authenticated to my VPN from an external network - all is good. I can restart with a connection to my internal WiFi and my VPN connection shows Internal (because I have Internal Host Detection configured). If I then open the GP app...
When I go to Monitor > Session Browser I still see active connections on the pasive peer. I verified it is truly the passive firewall and the other is active and that its supposed to be in Active/Passive mode in the HA configuration. Running the show session all command reveals the same thing. All time stamps are current.
Last weekend, I worked with a client to upgrade their Panorama (HA) from 8.1.6 to 9.0.6. Everything went smoothly. This weekend the plan was to upgrade the log collectors ( 2 M200s) When installing 9.0.6 on the log collectors it complained that the log collectors needed to have a more current version of content then they currently had. Unfor...
Hi, I am new to Palo Alto and want to do Palo Alto integration with our Panorama. need some guidelines for the same. and do we need to break HA for this process? Let me know if any other inputs.
Perform an upgrade from 8.1.5 directly to 9.0.6 yesterday on A/P pair of 5250. The HA2 link won't come up on 9.0.6 This is from TAC, Check the pan_dha.log in dp0-log and dp1-log for this error, I was able to see the following errors that explain as to why HA2 would not come up:pan_dha.log++++++++++++++Error: pan_dha_config_connection_load(pan_...
Hi All,Can we setup floating management IP so that I can always login to active device ? We do have option by setting management profile for interface, but looking for an option if we can set it up via management interface . Thanks
In one of our firewalls we have zone A which has network x.x.x.x/24, and zone B which has network y.y.y.y/24. There is a rule allowing traffic between them. Some high-ranking people at my company need to be able to block this traffic automatically at any time. I wrote a powershell script which is triggered by the incident management system when...
Hi,We have a shortage in Ethernet ports on a Paloalto firewallI would like to ask if it is possible to change a dedicated HA port to a data port (Layer3, Layer2...)? I know it is possible to change the type of a data port to an HA port.Thanks for your supportAli
| User | Likes Count |
|---|---|
| 2 | |
| 2 | |
| 2 | |
| 1 | |
| 1 |




