tcp out of order
I am trying to diagnose why I am unable to access some server via ssh and the VPN. I have done a packet trace and the results were concerning tcp out of order and retransmission. So what is the best way to find out why?
I'm trying to figure out whether our file size limits for WildFire are set appropriately. I have been unable to find a good way to determine whether there are files that aren't being uploaded due to their size. Would that show up in our logs? I've also discovered the WildFire logs don't include a column for file size, I need to look at the detai...
How do I get the signature on what a Vulnerability has triggered?I can only see the Threat Name and its ID in Panorama and look up the ID in the Customer Portal.But there does not stand what combination or findings actually lead to this attack. Where can I get this information? Thanks in advance.
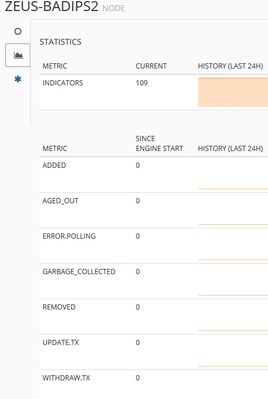
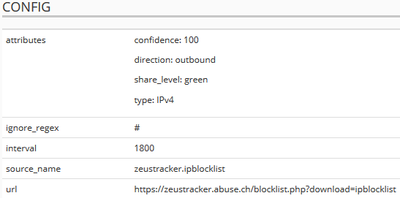
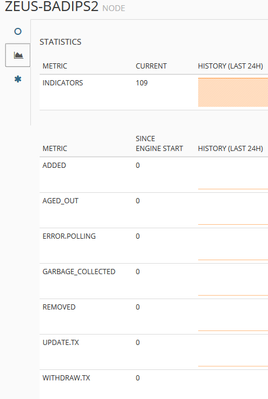
We pull Zeus IP's using minemeld. Statics page shows the current number of IP' 109, which is the same as hosted on this URL. https://zeustracker.abuse.ch/blocklist.php?download=ipblocklist Every few months i got notified to comunication with one of theses IP's and when i check the zeustracker.abuse.ch shows the IP in the list but the output is ...
Hello team! I hope you are doing alright. Currently, I am trying to add a customized miner prototype and while creating it in the /opt/minemeld/local/prototypes/ folder, I am not able to see in added in the GUI. What could be the problem here? Thanks in advance! Best regards, Petar
Hi I have to build up a IPSec tunnel with a partner. So at Network -> Interfaces -> eth 1/1 I have my connection to internet with a /28 Net. I call it for example 12.34.56.144/28 net. There the router from my isp is IP 12.34.56.145. I will build up my tunnel on ip .146. Now on the eth 1/1 I define the IP 12.34.56.146/28 so the complete /28...
First I would like to say that we are pursuing this with CarbonBlack and we have worked with PAN support already to see what our options are. This is as much an informative post as it is to see what other people think and are doing.For the record PAN support suggested changing the DNS entry from a lookup to a FTP file check. We would prefer to...
We pull Zeus IP's using minemeld. Statics page shows the current number of IP' 109, which is the same as hosted on this URL. https://zeustracker.abuse.ch/blocklist.php?download=ipblocklist Every few months i got notified to comunication with one of theses IP's and when i check the zeustracker.abuse.ch shows the IP in the list but the output is ...
i need help with understading how threat prvention throughput works ,i mean for all integrated features(ips,antivrus,..) what is the throughput of each alone ,as in specsheet only total throughput is mentioned
If you have two factor auth on the portal and the gateway without using the cookie or passing the auth from the portal to the gateway will it ask you to authenticate twice?
Hi guys, recently I've noticed a strange behaviour in my DShield miner (dshield.block prototype, https://www.dshield.org/block.txt). I have 2 MM (0.9.46 and 0.9.48), and both present the problem. Time to time, I can't precise the period, in fact it is not regular, my miner presents 0 indicators mined. First, I would like to know if somebody else...
Is PAN abondoning the GP mobile client on Android? The last update was a while ago, the UI is just horrid and it crashes under Android 9. Several reports of the issue have been made but all is quiet so far. Does anyone have any inside info? I was using XAuth but after upgrading to 8.1.3 I am getting funny behavior so I was going to give the GP c...
Hi, We have a inbound NAT for FTPS but the connections are not working. We can not see any deny in FWs.We dont have decrypt SSL configured. I think it shouldnt be necessary, right?Policy configures has "ssl" and "ftp" allowed. this is the ftp log: Why ftps connections are not working?? any dynamic port or something like that?
hello, I have a problem matching rules using user id, in uadebug.log I can se this warning:[ Warn 2813]: Device thread 1 replied get BloomFilter msg with no BFsomeone know what that means? Thanks
I had ssl decryption in place on PA_5020 and it seems like during peak times, my internal data traffic is reaching max ssl decryption session limit and those beyond the limit are shown as decrypt error and are sent un-decrypted. Is there any solution for this besides hardware upgrade, offload ssl decrypt to proxy? Thanks.