General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Headsup: AZURE VPN not comming up again, session discarding

Hi, I just want to share a problem i have been troubleshooting. I have lots of vpn's terminating on our FW, haven't had real problems until i started to connect Azure VPN's. After a network hickup they usually did not come up again. I had the hardest time in finding out why. It seems that Azure sends so many IKE initiation packets that if for so...
P.Braat by L1 Bithead
  • 2954 Views
  • 2 replies
  • 0 Likes

Log Card Interface Issues

We have configured a log card interface on one of our 7050 devices for submission to wildfire. This is not working. Our testing shows we cannot ping the default gateway conifgured on the interface. If we ping from the router, then no response is recived, but the packet count on the log card interface increases according for both recicieved and t...

HTTP OPTIONS Method

Hi,I am getting contionous 'HTTP OPTIONS Method' - alertWhat is the reason for thisIf I have multiple vulnerabilty profile ,I want to exclude this from one of the profile or one of the ip(I want to ignore this vulnerabilty checking in a profile or against an IP)How can i do that ?Thanks

simsim by L4 Transporter
  • 3387 Views
  • 3 replies
  • 0 Likes

cookie size

Hi, Is there something settings related to 'cookie size' in pa Thanks

simsim by L4 Transporter
  • 2081 Views
  • 2 replies
  • 0 Likes

Resolved! Path Monitoring Group Name field will not save?

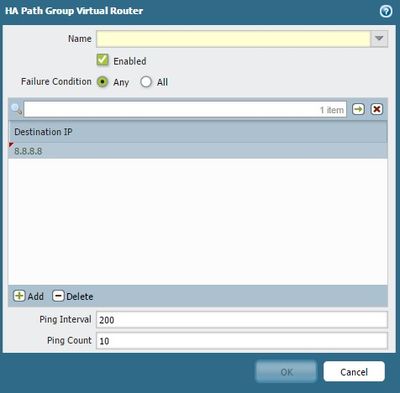
Hi folks, Another HA question, but seems like could be an easy one. I have one test PA-200 OS 6.1.4, enabled HA (for practice), created a Link Group, and now trying to create a Path Group.However, when I type in a name and click off of it, press enter, or click OK the text I typed disappears and unable to save it. I tried it on our production PA...

PathAny1.jpg
OMatlock by L4 Transporter
  • 2462 Views
  • 2 replies
  • 0 Likes

IPSec Tunnel PAN to Cisco ASA - matching for phase 2

Do the proxy ID's on the pan side have to match the ACL defined crypto domain on the ASA? That is - suppose on the PAN side you had for phase II of the tunnel 192.168.1.0, 192.168.2.0 and 192.168.3.0 while the ASA side had only 192.168.1.0 and 192.168.2.0. Would phase II tunnel still come and allow traffic for the first two subnets? Or would bot...

palomed by L3 Networker
  • 2860 Views
  • 3 replies
  • 0 Likes

Resolved! It's time to allow verified PAN customers to change URL categories for specific websites

Long time PAN Customer with huge PAN deployment, we have a very large user base and get multiple website blocked requests daily. We block Parked and Unknown domains for security purposes, it's worth it. However, there's a large amount of new websites that are rightfully listed as parked or unknown, then updated shortly after, then legit websites...

Rags by L2 Linker
  • 4839 Views
  • 5 replies
  • 1 Likes

Resolved! IPSEC site-to-site; passing ICMP only.. no other protocol (TCP/UDP)

I have an IPSEC-to-SITE.IKE Phase 1 and Phase 2 are good/live.Tunnel interface in right zone. Routes fines.Policy defined (app: any, service: any).I can see the policy being hit when I generate icmp/pings. And can get to the proxy id's/subnets on other side.I can't get anything other than ICMP through though.. No other TCP/UDP layer traffic.. ...

mpgioia by L3 Networker
  • 19804 Views
  • 20 replies
  • 0 Likes

API or script to report bad URLs to PAN?

Is there an ability to post bad URL reports to PAN in an automated/scripted fashion? I know the report site exists (https://urlfiltering.paloaltonetworks.com) but it requires a captcha. My goal is to write a script which takes in a (phishing) URL as input and automatically reports it to several security vendors.

Schuyler by L0 Member
  • 4402 Views
  • 3 replies
  • 0 Likes

Report issue - incorrect data

Hi All, i have a problem: when my customer generates reports there are problem with data, i see that the usage in one week is less than the sum of two random days in the same week.example:Week report: 450.5 G bytesDay X: 588.3 G bytesDay Y: 262.0 G bytes Has anyone some hints? Regards,Daniele

DKanta by L2 Linker
  • 2404 Views
  • 2 replies
  • 0 Likes

Recommended MTU for GlobalProtect Gateway

Hello, We’re experiencing slowness from global connect clients located offsite back to firewall (i.e. 5MBps). Without the VPN client, the user can get up to 60MBps. What is the recommended MTU settings for GlobalProtect Gateway/interface should be set at? Our Ethernet interface(1/3) MTU where gateway terminates in DMZ is set at 1350 and the tunn...

Farzana by L4 Transporter
  • 10879 Views
  • 5 replies
  • 0 Likes

Resolved! URL log forwarding to syslog servers, but not all informational threat logs.

we need to forward url filtering logs from PaloAlto to syslog server ( similarly from Panorama to syslog server.)To do this we need to to forward the Threat "Informational" logs ( generally url filtering logs are part of threat "informational logs ). But we do not want to forward all "informational" threat logs to syslog servers as it will add l...

URL Filtering from Internet Traffic to Internal Websites

Been doing some searching but havn't come up with anybody doing this and if it has other problems / security ramifications I'm not aware of. My problem:We have an employee that is no longer working at our business but there personal computer at home is configured to our internal mail server. I can see the spam of authentication attempts from the...

Resolved! HA Configuration question?

Hi folks, As I prepare for my first HA configuration next weekend, have at least one question today. I understand from reading that the configuration will copy over to the second passive firewall over the HA1 link.Does that include everything? Certificates as well? Thanks

OMatlock by L4 Transporter
  • 2239 Views
  • 1 replies
  • 0 Likes

Resolved! Destination NAT vs Source NAT with Bi-directional?

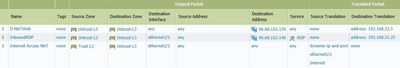
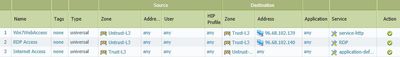
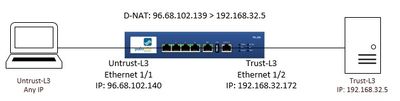
Hi folks, I am reading several articles about NAT types and bi-directional.I have a test going, but confused about how my web server is translating its source address when replying. I thought that I would have to create a bi-directional NAT rule to get the web server to change its IP back to public (after the D-NAT), but that's not the case. It...

visio.jpg
NATRules.jpg
Securityrules.jpg
web.jpg
OMatlock by L4 Transporter
  • 17490 Views
  • 8 replies
  • 0 Likes
  • 24450 Posts
  • 125 Subscriptions
Top Solution Authors
Labels