General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Panorama PDF Summary reports not providing data

I'm having some issues generating PDF reports in Panorama and after Google didn't help me, I thought it would be worth asking here. We've created some custom reports in the past, had PDF summaries generated, and the reports get sent out on a regular basis with no issues. We followed our usual steps to create the reports described below. Yesterda...
DNS Security

Hello FolksDoes anyone know why I am having problems with DNS Sinkhole when my computers have dynamic DNS, I have spent days testing and I have detected that with fixed DNS I see the log but with dynamic DNS I don't see any logI have applied the Security profile , Decryption rule, But the behaviour is the same. Also I have DNS Security license.T...

dae_sua by • L0 Member
  • 1943 Views
  • 1 replies
  • 0 Likes

MS-Teams issues with disconnections

Hi all, we have some issues with MS-Teams.Our customers have random disconnections during the cals. In the app they recive error - "bad network quality" and after that they reconnect. Call quality itself is good. In MS console there is no allerts for diconnections or bad quality. Evriting regarding MS products was excluded from inspecion decript...

stef by • L2 Linker
  • 4292 Views
  • 1 replies
  • 0 Likes

Resolved! SL Decryption Exclusions

Hi All,I'm using SSL decryption and if I wanted to have a URL in the exceptions (not decrypted) list, I would add it to a custom url category I created and just add the domain and apply the cutom url to the policy.But I also noticed that in Device>Certificate Management>SSL decryption exclusion - there are many predefined domains that seem...

roma by • L2 Linker
  • 2553 Views
  • 1 replies
  • 0 Likes

TCP Source Port Pass Firewall Vulnerability

Hi Team, We are getting below vulnerability in PA NGFW. Please find the error below, IP StatusQIDTitleTypeSeverityPortProtocolFQDNSSLCVE IDVendor ReferenceBugtraq IDCVSS BaseCVSS TemporalCVSS3 BaseCVSS3 TemporalThreatImpactSolutionExploitabilityAssociated MalwareResultsPCI VulnInstanceCategoryResult Errorshost scanned, found vuln34000TCP Sourc...

External user access to cloud app through firewall

Hello,Currently we are using an application hosted in cloud (Azure) which is being accessed by LAN users only through a Site-to-Site IPSec tunnel.Now we want to give access of this Azure application to external users(they don't have LAN access).We want users to go through the firewall. Any suggestions on how can we achieve this.

OFHydIn by • L0 Member
  • 1878 Views
  • 1 replies
  • 0 Likes

real time interface monitor

I have an interface connected internet line with bandwidth 10MB can i monitor B.w utlization real time , meaning can paloalto draw a graph time and b.w at every moment i can see ultization may 5 MB ..5.1MB 9MB or something like that . or i must use a netflow from paloalto and third party to draw this graph

PBF over VPN tunnel

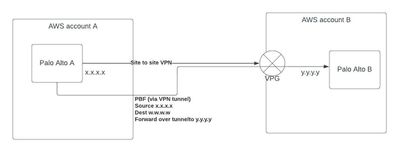
Hello, I try to create a route forwarding from a Palo Alto in one AWS account to a Palo Alto in another AWS account.The Palo Alto in account A is creating a VPN to a Virtual Private Gateway in account B. THe VPN is up and we can manage the firewall. When creating a PBF the traffic arrives on the Palo Alto in account A (in the monitor I can see ...

pbf.jpeg

lacp neg failed for sec then came up

got email alert SYSTEM ALERT : critical : LACP interface ethernet1/21 moved out of AE-group ae1. Selection state Selected system log shows ( severity neq informational ) and ( eventid eq nego-fail ) and ( description contains 'LACP interface ethernet1/21 moved out of AE-group ae1. Selection state Selected' ) and ( receive_time leq '2019/03/01 11...

MP18 by • Cyber Elite
  • 5778 Views
  • 6 replies
  • 0 Likes

IPv6 BGP issue: bgp peer ISP_IPv6_Peer local address 0:0:0:0:0:0:0:0 does not belong to interface

I had been troubleshooting the following error message when trying to add an IPv6 BGP peer to my PA:bgp peer ISP_IPv6_Peer local address 0:0:0:0:0:0:0:0 does not belong to interface ethernet1/1(Module: routed)Configuration is invalidFor some reason our configuration had IPv6 configured on all interfaces of the firewall but only the Trust interfa...

bspilde by • L4 Transporter
  • 5243 Views
  • 2 replies
  • 2 Likes

PA-220 is not allowing inbound traffic

HI PA Community! I have a very odd issue. My Palo will not allow any inbound connection. I was setting up GP and wondered why I can't hit the portal. Then realized I can't even PING the public IP. I am using a dynamic PPoE connection to my ISP. I created a special rule to allow my testing external computer and can see the rules being hit. I ca...

DJ_Palo by • L1 Bithead
  • 2182 Views
  • 1 replies
  • 0 Likes

Resolved! possible to unblock for one website - Block sessions with untrusted issuers?

Hello,On my "no-decrypt" policy - I couldnt find a way to exclude only a specific site from having an untrusted CA issuer. The only way to solve the problem and to be able to connect the device on our LAN to the website was to uncheck the box on the no-decrypt profile " Block sessions with untrusted issuers" - but now that opens up all of them.

roma by • L2 Linker
  • 3018 Views
  • 1 replies
  • 0 Likes

No way to unsubscribe?

The unsubscribe link at the bottom of the newsletter takes me to a page that only has a "Subscribe" button. An unsubscriber should not have to agree to Terms of Use and a Privacy Statement.

Easiest way to find and replace Interfaces

What is an easy way to find and replace Palo Alto interfaces? Let's say for example I am combining a bunch of interfaces such as ethernet1/9 and ethernet 1/10 into an aggregation group (i.e. ae1) and adding these as tagged VLANS i.e. ae1.123, ae1.456 Q: Is there an easy way to migrate over replacing the Interfaces for all the NAT rules, IKE Gate...

birkhojk by • L2 Linker
  • 3100 Views
  • 1 replies
  • 0 Likes
  • 24463 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels