General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! How to display more than 100 items in EDL

I need the whole output from an EDL but command only displays 10. Even in the rest API.GUI works but i can't export it form there.Source was deleted and now i need to restore all the entries in that EDL Total valid entries : 2295Total ignored entries : 0Total invalid entries : 0Total displayed entries : 100
raji_toor by • L4 Transporter
  • 5601 Views
  • 4 replies
  • 0 Likes

SSLlabs test is blocked on decryption with F5 passthrough

https://live.paloaltonetworks.com/t5/general-topics/extra-certs-inbound-decryption/m-p/457936Adding to the previous discussion with same setup where PA is doing decryption and the F5 is doing SSL bridging/offload while proxying for the server behind it. If we do SSL bridging/offload SSLlabs test goes fine with PA doing decryption and F5 will pr...

raji_toor by • L4 Transporter
  • 5692 Views
  • 5 replies
  • 0 Likes

Resolved! Management ip address cannot be seen again

Hi Management interface ip address is configured, and it could work before. but now I cannot see it. After the ip address is reconfigured(and commit), I still cannot see it. Below is its config. Anyone can take a look at it? Thank you! set deviceconfig system ip-address 192.168.1.6 netmask 255.255.255.0 default-gateway 192.168.1.1 show interfac...

Custom URL Categories - ending tokens

Let's say we want to match a domain in a custom URL category or EDL, including all sub-domains. While most people would expect "youtube.com" to do the job, in a PAN-OS this would only match youtube.com and not content.youtube.com. To achieve the result we must include:youtube.com*.youtube.comI can live with that... however in PAN-OS 10 admins ar...

mb_equate by • L3 Networker
  • 5505 Views
  • 1 replies
  • 1 Likes

QoS priority - 'real-time' vs 'high'

Hi, What is the difference between 'real-time' and 'high' priority than? Will there be any difference under similar circumstances when you have 100 Mbit/s MAX egress and 50 Mbit/s guarantee, while actual traffic matching this class exceeding 100 Mbit/s? Previously I was under impression that real-time one will just drop traffic exceeding queue l...

User Mapping on Mac with M1 chip in domain

Hi All,I joined Macbook on m1 chip to the domain and the firewall don't recognize user (Don't work user-mapping). I can't apply policy which works via users. We have 3 Mac's on m1 chip with the same problem. Also checked on Mac with intel - no problem with user-mapping after join Mac to domain. Maybe someone has already met such a problem. Thanks.

Newbie: VPN on PanOS 10

Hi everyone, This is probably trivial, but I am fairly new to this so bear with me:I would like to set up the PA firewall as a VPN server for users to connect to (ideally, using only the built-in windows client). After authentication they should have access to a couple of servers connected to a single network port on the firewall, but they shoul...

PANOS 9.1 know issue PAN-83610 network processor

PAN-83610In rare cases, a PA-5200 Series firewall (with an FE100 network processor) that has session offload enabled (default) incorrectly resets the UDP checksum of outgoing UDP packets.Workaround: In PAN-OS 8.0.6 and later releases, you can persistently disable session offload for only UDP traffic using the set session udp-off load no CLI comm...

VLim by • L2 Linker
  • 4461 Views
  • 1 replies
  • 1 Likes

Maintenance mode

When we try to access maintenance mode keeping "M" press the device just stop booting and nothing appears on console. Then if I press the M after some seconds just normal boot. We also try typing "maint" but no luck

v-ealva by • L0 Member
  • 3745 Views
  • 2 replies
  • 0 Likes

VWire Radius (NPS) via Mgmt

Happy 2022 ! We've just setup VWires for our branches firewalls (A/A Layer 2), no ip address on any interfaces except :- Mgmt (routable and managed by Panorama)- HA1-3 (non-routable address) Most of the device management (SNMP, NTP and etc via Mgmt IP) works fine except for Radius authentication, we did some troubleshooting :- tested on the fir...

annielee by • L2 Linker
  • 3448 Views
  • 4 replies
  • 1 Likes

Downgrade from 9.1.12.h3 version to 9.1.9

Hi All, I have decided to upgrade my Palo Alto 850 from version 9.1.9 to 9.1.12.h3 but after the secondary Palo Alto upgrade facing an issue where interface are not getting up so my team decided to roll back to version 9.1.9. Should my configuration completely wiped out if i downgrade my device ? or if no then what are the precaution i have to t...

PANOS 8.0.x restart IPSEC tunnels from GUI

Dear all, we found out that we are not able to restart VPN tunnels in PANOS 8.0.x from GUI because its grayed out and it is an expected behavior as you can see the message "Restart disabled because OK". The conclusion is that on version 8.0.x it's not possible anymore to restart the tunnel from GUI if the tunnel is up and running, but you can st...

Rboehme by • L2 Linker
  • 6005 Views
  • 3 replies
  • 0 Likes

Remote backup issue

I am trying to backup the config from a remote backup server. The backup file is generating but no config showing in the file. Instead when I open the xml file, I can see this " <?xml version="1.0"?> -<response code="403" status="error"> -<result> <msg>Type [export] not authorized for user role.</msg> " The st...

Kerberos SSO for Captive Portal

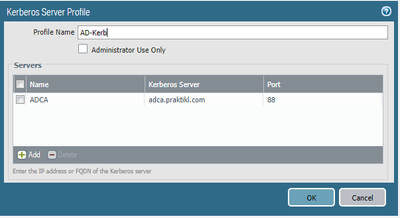
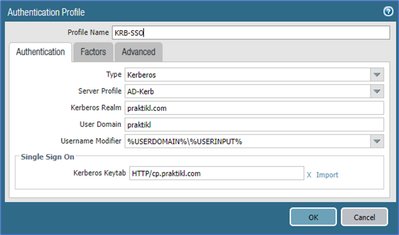
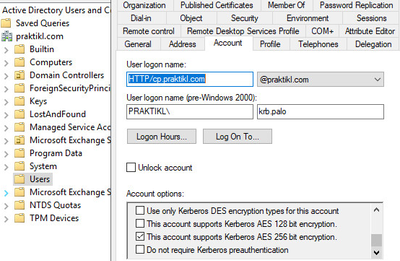
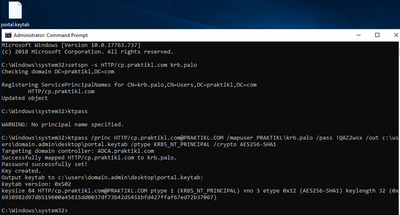
Been working through options for gathering userID data on non-domain-joined machines lately, so here's another complete option using Kerberos (krb) SSO. Create a user in AD (my example, username: krb.palo), check the boxes for:User cannot change passwordPassword never expiresThis account supports Kerberos AES 256 bit encryptionNOTE: this account...

jbworley_0-1641995839136.png
jbworley_1-1641995839170.png
jbworley_2-1641995839174.png
jbworley_16-1641997811010.png
jbworley by • L1 Bithead
  • 5931 Views
  • 1 replies
  • 5 Likes

Resolved! Best practice to write an application based policy whith some ports different from standard

Hello,I would need to write a policy to allow Oracle connection on specific servers.Unfortunately I have some Oracle instances that don't use the standard TCP 1521 port.How can I handle this problem writing just one rules that matches all my destination Oracle servers even if there are different port used? Thanks for your reccomendations Regards

MGatti by • L1 Bithead
  • 3949 Views
  • 2 replies
  • 0 Likes
  • 24482 Posts
  • 125 Subscriptions
Top Solution Authors
Labels