Using PA-3220 for URL filtering to replace Barracuda Web Filter
We just got our PA-3220 and hoping to use that for our URL/Web filtering and discontinue our Barracuda Web filter. Has anyone implemented the URL filtering with terminal server users?
I made a big mistake and not sure how to correct it. We have a Palo Alto Firewall. I wanted to white list an IP address so my PCI Scans would not fail. I found an article but it seems it lead me a totally different direction. It had me put the IP in the Trusted IP list on the Management Interface Policy. Now I can't login or even ping the P...
Currently I have GlobalProtect Gateways on each of my ISP links which requires dedicated IP space for the clients according to PA documentation that client space IP pools shouldn't overlap. I've recently been asked to grow the remote access pool to a fairly significant number. This would require a second large chunk of addressing that would larg...
Hello everyone We have configured active-passive HA on a pair of 5220 I have configured link monitoring I need to migrate the HA links of the FW , all except the backup HA1 management one. What would be the best procedure to prevent them from becoming active? Is there any way to check end to end after each change, apart from looking at the link ...
Hi everyone, I wanted to let you all know that Palo Alto Networks is now accepting Papers for the Ignite'21 Conference! Palo Alto Networks is looking for speakers and presenters with highly technical backgrounds who can share their experience and expertise around groundbreaking new threat research, innovative best practices, and next-gen cy...
Is it possible to have a failover PBF on a AE interfaces?
Hello Guys, One of my client is received the logs of data filtering with license-expired category. How to troubleshoot this issue?
One user of our company has an issue connection to the GlobalProtect Gateway using IPSEC, but there is also no fallback to SSL.His ISP carrier is using "Carrier Grade NAT" and this is likely the cause of his issue. I know that we can force SSL connections on the Gateway, but this is a global setting and will be affecting all users, I just want t...
I want to check all my object addresses with zero traffic to clean up my flow rules. Can I replace my sources and destination IP with an "all IP" setting ? Can you help me ?section "Query Builder" does not work (see image)
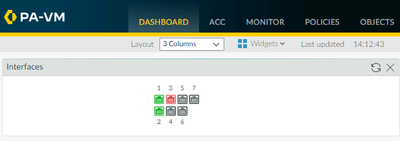
Hello, For testing purpose, I added VR and Zone to Eth Interface1/3. I have removed everything from it but in the Dashboard it shows Red color. This creates confusion as some think the interface is down even though nothing is connected to it. Is there anyway to turn it back to gray?
Multiple questions - Recently we've found that traffic not within a URL category specified in a rule is being allowed. The rule appears to be allowing the traffic as the session starts and ends with the action of allowed determined. Would using the same category within a URL filter differ than only having a category configured? It's my understan...
We have outbound decryption working but there are few sites that popup that donot work from time to time and have to add the to exceptions. I am trying to investigate a recently highlighted website and to learn how to troubleshoot this better. If I run this openssl command connection on the client is successful and wireshark output looks like th...
Is there a way to limit /throttle qos per device? Outside of making a QOS rule per subnet or ip host? I know on some platforms there is a way you can limit every client to a max of 500kb/s per device. Is there any easy way to do this with the firewalls? I do see the below link, but that is more related to the entire subnet vs. per host lim...
Hi All, We are planning to migrate from PA-500 to PA-220, and there are some concerns to verify. Here are our current versions. My concerns are, 1) How we can match the OS/Content versions with the new PA-220?2) What will be the migration procedure from PA-500 to PA-220?
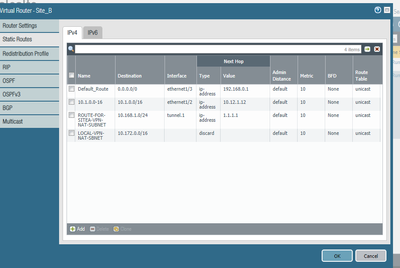
Hello Experts, I am new to PA and trying to understand how below can be achieved. I am trying to set up IPSec tunnel between checkpoint and PA.Diag: I want to establish a IPSec tunnel between CP and PA. On PA side i have 172.16.0.0/24(inside zone) private IP range which i want to NAT to 10.172.0.0/24 and send it to CP side as intresting traffic....
| Subject | Likes |
|---|---|
| 5 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 5 | |
| 4 | |
| 3 | |
| 2 | |
| 2 |