General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! Using the Panaroma as a central manager for Cisco AnyConnect.

Team,Any one aware if we can even use the Panaroma a a central manager for the Cisco AnyConnect firewall?My use cases are: 1. Central management and to push policies to the Cisco AnyConnect. 2. Ensure policies are in sync and same across all AnyConnect nodes.3. Possible backup of the Cisco AnyConnect configuration.4. Possible historic logs stori...
nson2139 by • L3 Networker
  • 3028 Views
  • 1 replies
  • 0 Likes

FW has stopped recognizing several users and does not map them with the corresponding domain group, so it does not apply the necessary policies.

Hello,We have changed a 2 palo alto 5220 in cluster for another 2 palo alto 5250 version 8.1.16.We have migrated the configuration by exporting and adapting the xml.Everything works ok except for a detail in the new passive fw. we have detected it when switching and testing.The fw has stopped recognizing several users and does not map them with ...

BigPalo by • L4 Transporter
  • 4632 Views
  • 3 replies
  • 0 Likes

PXE boot not working through FW

Hi all,I have a FW with PanOS 9.1.7 that is causing PXE boot issues with TFTP protocol.When traffic is not routed through the firewall it all works and I have seen several threads about this problem but no solution. DHCP server: Windows Server 2012 R2 172.18.76.23WDS server: 172.18.76.20 DHCP option 66: 172.18.76.20DHCP option 67: \boot\x64\wdsn...

Resolved! Azure HA not coming up

Do I need license to test Azure HA scenario. I am following all the steps but HA1 doesn't come up.I don't have any licenses. And doing a test run of implementation as HA active/passive.Default 10.0 gets installed with BYOL, but we don't have license yet.

raji_toor by • L4 Transporter
  • 3265 Views
  • 2 replies
  • 0 Likes

Resolved! Finally have pre-login working - but now

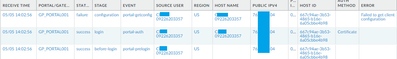
I'm excited to finally have pre-login working per the logs below. But after the successful certificate based pre-login, portal-getconfig fails. On the pan the error message is "Failed to get client configuration". Any advise on how to troubleshoot this further is appreciated!

MichaelMedwid_0-1620266069104.png

SSL Decryption Issues - MacOS Big Sur 11.2.3

We have had SSL decryption configured since we deployed Palo Alto firewalls and it works with little issue on our Windows OS platforms. We have a new project to deploy a few MacOS clients as the application development team requires the ability to test Safari browsing of some web apps. Our internal Root CA has been imported into the keychain an...

How long time will need to prepar the PCNSA

Hi everyone I would like to prepare the certification PCNSA.My idea is to pay the tax exam as soon as posible will make force me to study the exam. I would like to know how many hours and time will need for I am going to the exam. Regards

Athan123 by • L0 Member
  • 6331 Views
  • 2 replies
  • 0 Likes

Resolved! 2 ISP NAT question

Hello, we have 2 ISPs . .Static route with metric 10 for the 1st one and another static route with metric 20 for the second one .We have 2 nat rules for LAN. 1st one is via ISP1 and 2nd is via ISP2.So when we change the default route we need to reorder the NAT policies in order to have internet.Is there a option to change default routes without...

stef by • L2 Linker
  • 2701 Views
  • 1 replies
  • 0 Likes

PA Destination NAT

I have a use-case that all subnets/VLANs should be able to access the server (192.168.4.4) via HTTP using the loopback IP address 192.168.6.2/32. The PA firewall is the gateway for all the VLANs. I would like to confirm if this is possible? The source will be VLAN 5 or VLAN 10 and destination is VLAN 20's loopback IP 192.168.6.2/32 using HTTP se...

Nikko by • L1 Bithead
  • 3372 Views
  • 2 replies
  • 0 Likes

Resolved! Aplicação incompleta

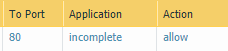
Galera, boa tarde. Estou com um problema bastante confuso, tento acessar um determinado site "HTTP" é recebo a erro (Não é possível acessar esse site), realizamos um teste fora da nossa rede é o acesso é realizado normalmente. Analisando os LOGS verifiquei que recebemos a ação incomplete.O que estamos fazendo de errado ?

Lucaaslr_0-1620676620608.png
Lucaaslr by • L0 Member
  • 2902 Views
  • 1 replies
  • 0 Likes

application

Guys, good afternoon. I have a very confusing problem, I try to access a certain "HTTP" site and I get an error (It is not possible to access that site), we perform a test outside our network and the access is done normally. Analyzing the LOGS, I found that we received the incomplete action.

Lucaaslr_0-1620677681082.png
Lucaaslr by • L0 Member
  • 3213 Views
  • 3 replies
  • 0 Likes

User-ID only tags IPv4 or IPv6 address in dual stack

I've got the User-ID agent installed on three servers and I've recently began enabling IPv6 internally and I've noticed a problem. The traffic logs in Palo Alto only associate either the IPv4 address or IPv6 address of a machine with a username depending on what is the preference in Windows. How can I get the username to be associated to both ...

Lcroce by • L1 Bithead
  • 5678 Views
  • 3 replies
  • 1 Likes

can MineMeld be installed on ubuntu 20.04?

I'm getting this error, how do i get around it? $ sudo apt install -o Dpkg::Options::="--force-overwrite" -y minemeldReading package lists... DoneBuilding dependency tree Reading state information... DoneSome packages could not be installed. This may mean that you haverequested an impossible situation or if you are using the unstabledistributi...

Thyrion by • L2 Linker
  • 5028 Views
  • 2 replies
  • 0 Likes

NGINX configuration for SSL Inbound Inspection

Hello everybody, I'm trying to enable SSL Inbound Inspection to decrypt traffic to an internal webserver that runs on NGINX. I have already added the server certificate and key, and set up the corresponding decryption policy. The problem is that the firewall is not able to decrypt the traffic due to unsupported cipher, so I'm trying to force t...

grenzi by • L3 Networker
  • 4699 Views
  • 2 replies
  • 0 Likes

Resolved! RHEL7 - /bin/sh ./configure Permission Denied

Hi all,I'm installing minemeld-ansible on Redhat 7.When i run this command:sudo ansible-playbook -K -i 127.0.0.1, local.ymli got this error:`PLAY [minemeld playbook] *************************************************************************************************************************************************************************************...

  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





