Mac OS Big Sur support
I have accidentally upgraded to Mac OS Big Sur, since then Global Protect app is not able to connect to VPN. Should I expect Global Protect to work on Big Sur already? Or is it on the way? Thanks
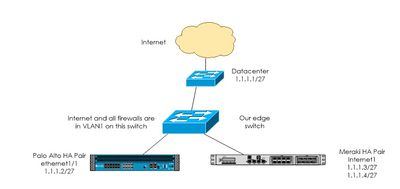
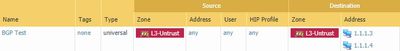
We currently have this setup in our datacenter. The Meraki HA pair is the VPN endpoint for our 120+ remote sites. In a DR situation the datacenter has IP mobility, where our current static IPs will failover. This setup uses BGP through the Palo. With BGP enabled on the Palo HA Pair and datacenter’s internet the Meraki HA pair is inaccessible, wh...
Hi.Can i allow videos from specific youtube channel and block others. Example I want to allowing all videos on Cisco channel (https://www.youtube.com/user/Cisco) and block all resource.
Hi Peeps,I got technical query regarding how to change SSH v1 to SSH v2 in PA firewall, Because one of our customer got an alert from VAPT tool like as follows,. Description :- KPMG test team observed that the Secure Shell protocol version 1 support was enabled on the tested devices.Secure Shell is typically used as a cryptographically secure ...
I've configured a data filtering profile and have been testing sending the data filtering detections to syslog, then to Sumologic. From what I've read, these detections are Threat Type, Data subtype in the logs. I have a log forwarding profile created to send all Threat logs regardless of severity or app to syslog and can see types like vulnerab...
Hi all.I wonder PA can log a IP and mac address of spoof attack such as ip spoof, arp spoof, dns query spoofing attack.Sometimes, customer want to know above information from PA.I think PA only drop a wrong packets. isn't it?Thanks.Regards.Roh.
We are starting to see valid websites showing up as malicious due to them being hacked or for some other reason. Once the site is cleaned up however, is it up to someone in the Palo Alto community to request a URL Category change manually, or is there an automated process that checks the website to see if it is still malicious? or another way to...
Hello There, What is the best practice to block YouTube, Instagram for mobile apps? So far I tried to create an application base and custom URL policy to deny YouTube, Instagram. It works (deny access) if you access the site via HTTPS (Chrome, Firefox), but it won't work if I access YouTube, Instagram on mobile app. Thank you in advance
Hello Bros, I have an unlicensed and out of support single paloalto 3220 appliance, and this device is not licensed now as we have upgraded to paloalto ha.my question is I wanted to re-use this appliance for some network services such as nat and routing within the network. is this possible to accomplish without any licenses?TIA
We are having difficulty with our Active/Passive pair of PA_820’s where they are setup to allow auth to GlobalProtect based on AD group membership.If we create a new OU in AD and move a user to the newly created AD OU whilst still having the same group membership, they can no longer auth to connect to global protect from internal nor external ne...
Hello,we want to include a (external or internal) website via iframe in the welcome page. My test HTML site:<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Frameset//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-frameset.dtd"> <HTML><HEAD><TITLE>Palo Alto Networks - GlobalProtect Welcome Page</TITLE><meta http-e...
We have a pair of PA-3220 running 9.1.6. We made a config change on the passive and now not able to access the active firewall. Config was added to passive host where we added ssh ciphers / mac / host key to the mgmt interface. After the change we could access passive device (where the config was added) after a putty upgrade. We were not abl...
Hello, Is it possible to hardcode speed/duplex for 10G SFP port on PA-5220 device? i am getting below error: >set network interface ethernet ethernet1/5 link-speed 10000 link-duplex full Error: Server error : ethernet1/5 -> link-duplex 'full' is not a valid reference ethernet1/5 -> link-duplex is invalid I have gone through the article...
Hi All, I have a security rule to allow ip "A" to ssh to ip "B". I can see the traffic actually hitting the fw but it gets dropped with interzone-default. The test policy match also verifies that it matches the traffic. IP "B" is actually the firewall. And IP "B" is nated like this: original packet source IP "C", original packet dest ip "A", tr...
Hi all,Our developers are connecting from Zone1 to Zone2 with tcp (on ports between 2000 and 3000)The tcp session timeout on firewall is 3 hours.The security policy allows any application, any port from Zone1 to Zone2. But there are all default security profiles applied on that rule.When going to Zone2, the source IP is NATted to the firewall in...
| Subject | Likes |
|---|---|
| 3 Likes | |
| 3 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 4 | |
| 3 | |
| 2 | |
| 2 | |
| 2 |