PAN-ENT-PLAT-ESA-TT-1YR
Hello Dear All, Can you provide me with specification documents for these part numbers:PAN-ENT-PLAT-ESA-TT-1YR, PAN-ENT-PLAT-ESA-TT-3YR, PAN-ENT-PLAT-ESA-TT-5YR?Appreciate your fast responseThanksAhmed Sabry
I have two gateways where users are predominantly using split-tunnels. When I connect to Gateway A with a full tunnel, I can load public webpages and intranet sites. When I connect to Gateway B with a full tunnel, I cannot load public webpages like cnn.com, traffic logs show application incomplete to untrust zone, and traffic to the trust zone ...
Just setup a new VM-100 device in Azure. SSL decryption and security policies are in place. My test client PC can browse the web, and all of the policies seem to work. However, I cannot ping or tracert to any public website (e.g., www.apple.com). The DNS resolution works, I see that the ping traffic is allowed in the monitor tab, and I disabled ...
Can we disable the global protect portal & gateway and reactivate it whenever we needed it instead of deleting it entirely? We are using 9.1.3
We are going to configure Active-Passive HA for PA3250. Primary and secondary device both at different locations , distance - 25 Kilometer.Location A ( Primary FW) --- L2 switch -------------P2P link 60 Mbps-------------------------L2 Switch -------Location B ( Secondary FW)For above scenario , can we use common P2P link for HA1 and HA2 ? We wil...
Dear,I have a PAN 3220 that has failed and I have not been able to back up to put another PAN 3220 that I have as a spare, which they recommend ? Swap the Disk ???
This website appears in the URL filtering tool as having a problem which is not true https://epsfeg.org/So we need your help to remove it from the list
Hi,I am having an issue with PA-220 appliances attempting to contact wildfire cloud. They do not have Wildfire license, but are attempting to register at wildfire.paloaltonetworks.com. The issue is that the firewalls are attempting to set up this connection and generating a lot of unnecessary traffic. How can i stop the firewalls from attempting...
Hi, Like everyone, we have a lot of folks working from home. We use a CRM system called Ajeera, and in order to load up the various modules, the client system downloads an app from the server, which includes a .dll file. In the office, it works just fine, over VPN the .dll file is blocked. (It's a "ClickOnce" app, which is a new term to me, but ...
Hi, I am working on a Palo Alto Networks Firewall migration project. I exported and imported the configuration with a few errors that I fixed and when migrating from the old to the new PA-3220 firewalls. All internal communications wtih LDAP and other servers are working and the routing protocols are coming up internally and externally. I can al...
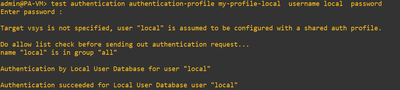
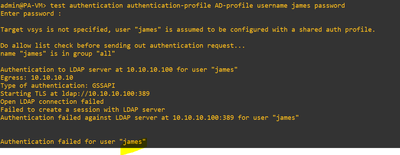
Hello,I have integrated the AD with Paloalto , it is working fine and i can see the IP user mapping is correct, once i tested authentication profileI got the below error:- Once i tested the authentication by local profile it is working fine. Can anyone help me on this to reolve this issue.
Hello, Community. Do you know if is there a way to change the "level admin" of an AD's user? In Device > Administrators I can't see the firewall's admins. Just the "admin" account. If I try to create a new account, I can't do it. The LDAP users can manage the firewall but they are not "Super Users". Currently, we have 2 firewalls in HA, conn...
I have tried for over a month to install Global Protect and have it work, and can't begin to count on how many installs/uninstalls of Global Protect I have done. Many people have tried to offer suggestions and it seems like the root cause is the PAN GP VNIC driver cannot be installed. When I try to install it manually via the inf, I get an Acces...
I have tried https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClKTCA0https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClQWCA0but still send/receive message via skype I don't implement ssl decryption PA-850Software Version:9.1.3-h1Applocation:8300-6225(07/31/20) Tks
we have a legacy client which supported only TLS(1.1) & need to connect to server in cloud which works on TLS1.2 only .. So If we do a SSL Decryption in pan firewall does pan will allow tls1.1 between client and pan firewall and tls 1.2 between pan firewall and cloud server ?? Dinesh
| Subject | Likes |
|---|---|
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like |