General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Panorama: Device group can't view addresses nor zones in sec policies

I recently added a template and device group and associated them with two new PAN 3020s. The template and the device group were clones from similar environments. When I try to edit a security policy or add a new policy and go to the source or destination and try to add a zone or address, there is nothing in the drop down box. Things i have tried...
palomed by • L3 Networker
  • 6944 Views
  • 5 replies
  • 0 Likes

Resolved! HA HSCI 3220

I have a pair of 3220s I'm configuring in HA active/passive. We connected the HSCI ports and got a green light on the ports and showing green/up on the HA dashboard widget. They are direct-connected and configured as Ethernet. Do I need to set an IP address on these for this config or are they good to go?

Traffic pattern of threat ID 38643

Wavelink Emulation License Server HTTP Header Processing Heap Buffer Overflow Vulnerability' generated by PAN NGFW detected on host 10.10.10.1. " Vulnerability Exploit Detection (hostname:8081/)"We have customer asking what is the traffic pattern that triggers this.What is the traffic pattern that triggers this alert?We are trying to narrow down...

Resolved! PanOS CLI show tags?

I can tag a rule via CLI, but how can I ask Panorama to show me rules tagged with tag-name? set device-group DG-Name security rules "Existing-rule-name" tag tag-name

BoDollis by • L1 Bithead
  • 5310 Views
  • 1 replies
  • 0 Likes

Redistributing default route into EBGP and IBGP not working

I am trying to redistribute default route into EBGP peer it is not working. 1. Created Redistribute profile to redistribute default route2. called redistribute profile under bgp redis rules3. Checked allowed default routes to redistribute3. created export policy to export 0.0.0.0/0 with action allow. Looking at below command we see export polic...

Whitelisting messenger-app

Hi guys, Goal: Whitelisting messenger app in mobiles but deny facebookDo you have any problems in whitelisting messenger app in a mobile? It seems creating a policy and allowing facebook-chat is not working.But if i included facebook-base it will work. Unfortunately clients will be able to use the facebook appIf you have work around kindly comme...

RemusDV by • L1 Bithead
  • 3543 Views
  • 2 replies
  • 0 Likes

Useless PBF warning

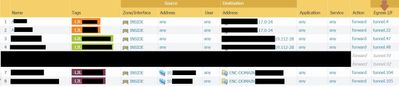
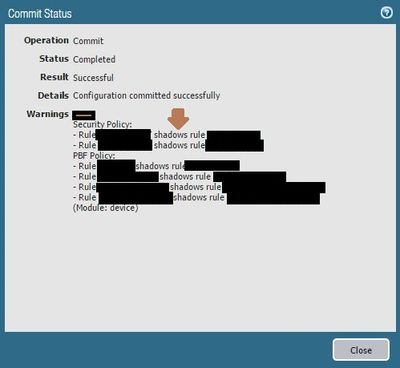
Hi All, That's not an issue.. I just want to share with you this thought Starting from the fact that the egress interface is NOT a matching criteria.. But I have to configure around 80 VPN tunnel (with their own backup tunnel using pbf option "disable if unreachable") .. so it means I will have 80 warnings.. :,( It should be useful to put egress...

PBF_warning.JPG
Warning_Rule.JPG

Block traceroute

Hi all,is there a way to block IP source if I match traceroute App-ID? Maybe with a custom vulnerability?

s_quasar by • L3 Networker
  • 8565 Views
  • 7 replies
  • 0 Likes

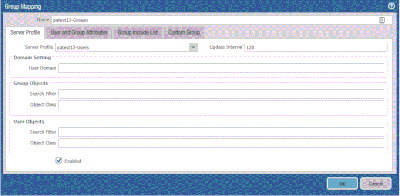
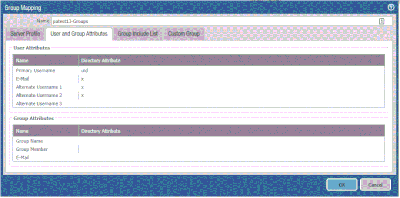
FreeIPA LDAP group mapping

UPDATED:The LDAP package FreeIPA uses , 389-ds-base, had some security vulunerabilities and has been updated. This update has caused the PA to fail checking users within groups. Here's is the latest configuration that works with 389-ds-base (1.3.8.4-15.el7.x86_64)Ive tried many parameters trying to connect to FreeIPA for LDAP group mapping and f...

FreeIPACapture1 (1).GIF
FreeIPACapture2 (1).GIF

can't login to web console

I have just instaled MM on Ubunto 16.04. Using these instructions: Howto on Ubuntu 16.04 $ sudo apt-get update $ sudo apt-get upgrade $ sudo apt-get install -y gcc git python-minimal python2.7-dev libffi-dev libssl-dev make $ wget https://bootstrap.pypa.io/get-pip.py $ sudo -H python get-pip.py $ sudo -H pip install ansible $ git clone https://g...

Mattk by • L2 Linker
  • 13656 Views
  • 8 replies
  • 1 Likes

Resolved! Firewall upgrade/replacement

What is the easiest way to replace old hardware(5050) with new(5520), that are in HA pair. Can i add 2 new firewalls to the HA group and failover. Or do i have to replace passive with new, make it active then remove the other.

raji_toor by • L4 Transporter
  • 10092 Views
  • 4 replies
  • 0 Likes

URL Response Page for SSL without decryption

Hello everyone, we have PA7050 managed by panorama. We dont have SSL decryption but we want to serve users a block url response page for https traffic. For that I followed following link: https://live.paloaltonetworks.com/t5/Configuration-Articles/How-to-Serve-a-URL-Response-Page-Over-an-HTTPS-Session-Without/ta-p/55998 But this doesn't seem to ...

Report mismatch

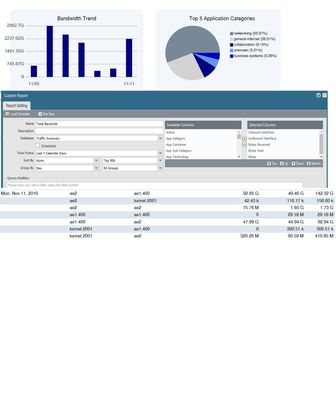
We are facing issue with mismatching of bandwidth statistics between our weekly report and custom total bandwidth report. For example, on 11 Nov the bandwidth shown on the weekly report is around 2000GB but the one shown on the custom total bandwidth report is a lot less than it. Any help on how to resolve this issue please?

Report.jpg
  • 24472 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels