Resolved! CDR report
Did anyone receive a threat report from palo alto and hushly? "Here is your Palo Alto Networks - 2018 Cyberthreat Defense Report you requested"
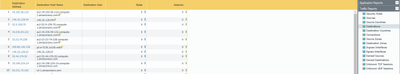
This probably has a very obvious answer, but google searches for the solution wound up showing me irrelevant pages...probably my fault as well. I am running various traffic reports, and all of them lack value in the bytes field. Any idea what is wrong?
I have got PAs in two DC, each DC have PA in active-passive unit, when I commit to one of the pairs in one of the DC, the committ is stuck at 0%. I see the Panorama is connected to "Passive" FW instead of the active FW , could be the reason why the commit is stuck at 0%.Does the Panorama have to be connected to the active unit for the commit to ...
Hello [Failure event]In the case of O365 's xml format, when MineMeld received traffic after ClientHello, I got a list but if I set config for JSON support I can not get a list. [Prerequisites]MineMeld will go through Paloalto and do Internet communication. [Question]I think that the packet flow that can be checked with Paloalto is incorre...
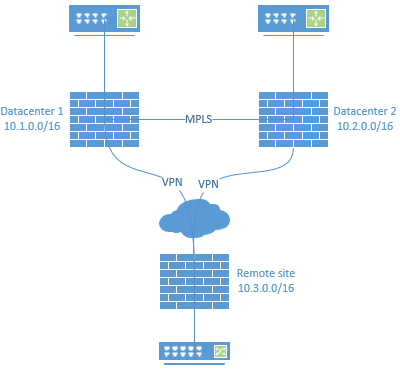
I'm trying to solve a routing conundrum to improve a remote site and provide redundancy, and hoping others may have some solutions. The short version is that we have the remote site with basic commodity internet using VPN to connect back to two datacenters. The datacenters in turn have direct links to each other, and all are running OSPF. The is...
Dear Sir,I am beginner in 802.1x authenication and paloalto.So please help explained and guide.I want to use 802.1x with MS CA.Can i use paloalto firewall as a policy enforcer for 802.1x authenication ?can use PA as a radius server for user log and mornitor ?
Migrating a Cisco fw to a Palo Alto and the Cisco has the ability to authenticate users to external Radius for FTP transfers based upon policy rules - the end user simply gets a user name and pass prompt which works across all platforms and can be scripted for automation. I know the Palo Alto has the ability to auth requests that are web based ...
I am testing Multi Factor Authentication with Okta. I have configured everything (including certificate profile) as per the guide as well as Okta specific YouTube video, The first factor (active directory auth) is working fine, however, I am getting "SSL Connect Error" in the authentication logs. I could see the 443 connections going to Okta. Ho...
All, I have an Arris (BGW210-700) set up as 192.168.2/24 (DHCPed) and have successfully configured the IP Passthrough to the PA-220. However, I am unable to get outbound from the PA-220. Has anyone run across this? I have the Arris going into 1/1 (as WAN), and then providing internal routing / DHCP, etc. This was working when I had Frontier / V...
We are looking to configure the firewall rules where if a known user fails the HIP check, the user has access to only the internet, and not the intranet. I currently have the rules configured such that failing the HIP check allows the user to access to both the internet and the intranet. We tried blocking RFC1918 in the destination address field...
Hello, I am using Pan-configurator to create some scripts, and i am wondering how to update predefined.xml file. Can we update this file manually or automatically? Kind regards.
Hi, i need Hardware Capabilities ( type of Cable, Chassis Height , Data Ports , managment ports ... ) of Palo alto PA-5050 to install in Data center of our customer in cluster with two WLC. Thanks,
Hello,I have an IP pool for GP users and IP are no being clearing when users disconnect the VPN, to clear this IPs we have to reboot the FW,Is there other way to clear this addres ? this must be cleared automatically after disconnect? Regards
My PA NGFW managed to setup VPN tunnels with AWS VGW. AWS given 2 sets of VGW where each of the VGW comes with 2 links that will connect to NGFW 2 ISP link respectively with different set of public IP Address.. Below are the setup flow:NGFW ISP1 -> AWS Tunnel1 (vgw1)NGFW ISP1 -> AWS Tunnel2 (vgw1)NGFW ISP2 -> AWS Tunnel3 (vgw2)NGFW ISP3...
Just getting my head around the ins and outs of Palos, and some initial lab setup we had leveraged a couple of PA-220s and a virtual instance of Panorama. Using that config, I'm building a standalone PA-220 and want to recycle the bulk of the config from what I'd tested with, however, importing that is shown as the config from Panorama, which w...
| User | Likes Count |
|---|---|
| 2 | |
| 2 | |
| 2 | |
| 1 | |
| 1 |





