Does PA supports Agentless Remote Access VPN
Hi All, Please let me know, whether PA supports agentless(GlobalProtect) remote access VPN? With SSL or IPSec. If it supports, please let me know how to configure it. Thank you in advance..

This is a fork of https://live.paloaltonetworks.com/t5/General-Topics/Statistics-reports-on-how-much-SSL-traffic-you-got/m-p/67945 but with a specific question. Dealing with reports in PA I wonder if the counters/statistics regarding appid ssl includes other appid's who also use ssl such as gmail-base, facebook-base and the others? That is l...
We started getting complaints from users that various Google services were showing intermittent disconnects. I think we've tracked it down to the QUIC protocol not being accurately identified by the PAN firewalls and getting blocked. I see 443/udp traffic from the hosts in question getting dropped as "unidentified-udp" mixed in with the allowed ...
Is there a way to export the current Security and NAT Policies to CSV, or even just PDF? I need to clean up a dirty firewall that I inherited, but I need other teams to let me know what is active/inactive. Screenshots or CLI outputs can work, but I want to provide this in a clear table format that is usable. I'd also like to know if there i...
Hi, any of you who knows if there is a whitepaper or such on how to generate a report or otherwise pick out the numbers/figures/graphs for how much SSL-traffic you got vs non SSL-traffic through a PA device? That is both in bandwidth and number of concurrent sessions over time.
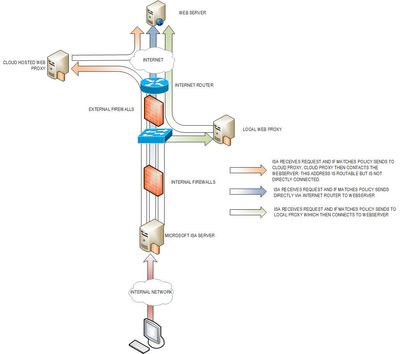
Hello All, Was just wondering if anyone may be able to help with this our question. Please see the attached High Level Diagram. Both Firewalls are PA 3020's with the full licence set enabled. We need to replace the ISA server which is not providing any other functions than forwarding the traffic down one of the 3 paths in the diagram, unfortun...
The scenario is 3 firewalls, with PA-HO acting as the hub and PA-1 and PA-2 as the branch sites. The Branch sites connect to the head office network via ipsec tunnels to PA-HO and vice-versa. Due to multple dis-contigous subnets on the branches, it was decided to use 0.0.0.0/0 proxy-ids for the tunnels. This was proven to work for the PA-HO and ...
Hello. I want to know my question what address and EBL maximum from you. 1. https://live.paloaltonetworks.com/t5/Configuration-Articles/Using-IP-Address-Lists-on-Palo-Alto-Networks-Policies/ta-p/57411 The above documnet describes " Each imported list can contain up to 5,000 IP addresses (IPv4 and/or IPv6), IP ranges, or subnets." How many c...
Hi guys Anyone know where is the path where the logs are stored FW CLI ? I hope your commentes regards
Hi, My query is about how the Palo Alto firewall timestamps logs when it sends them to a syslog server. Does it stamp the logs with UTC (GMT) time or does it use the configured local time as the timestamp? I notice when reviewing logs on the device it uses local time, however I'm unsure what they use once sent off the device. Thanks.
While troubleshooting a user's inability to connect to GlobalProtect, I wanted to verify there were IPs available. However, the IP pool did not appear under the DHCP servers. How can I check to make sure there are IPs available within the IP pool that was assigned to the GP Gateway?
Is it possible to send the syslogs for only the system changes from the pa to solarwinds? How to you configure the PA to send the change logs to solarwinds?
This is a new deployment and testing decryption. I have generated a self signed cert from the firewall and imported it into the local trusted root authority store on my computer. If I try to go to a site that is encrypted (eg https://www.google.ca ) I dont see my browser using the PAN cert (the cert used instead is the external Google.ca cert)...
I have been tasked with modifying our Captive Portal, from Palo Alto, that current users see when they connect to our guest Wi-Fi here at the Upper Canada District School Board. I have read most of the documentation related to the captive portal and what can generally be done with it. Now, I have already managed to change the style of the portal...
I have a customer that is using a PA-5020, and when users try to go to certain Outlook Web Access sites, it won't work for them. Checking the logs, I can see where the user initiates a connection over port 443 to the destination OWA server, but App-ID identifies it as 'unknown' instead of 'ssl'. I never see the SSL setup, and the user's connec...
| Subject | Likes |
|---|---|
| 2 Likes | |
| 2 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |




