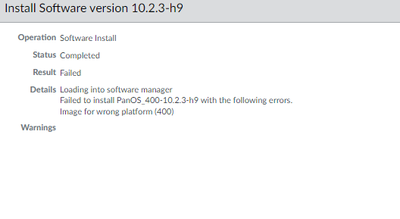
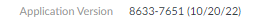10.2.3 Software Update Install Error
The firmware is not being updated. The question is the application version. Is there any way to solve the problem?
Wish to configure new VSYS, will it cause any issue while configuring? Do we need to reboot after enabling Multi-vsys opention? Will it will cause network disruption over default VSYS1? · Will it will affect the functionality of Access Control Policy on the default VSYS1? · Will it will affect the entire functionality of default VSYS1? · Could...
Hi, Yesterday we upgrade Pan-OS version from 9.1.13 to 10.2.6. GP version on 5.2.12. Now we have issue with GP as we have difficulties to connect the Gateway with error Cookie expired/Authentication failed We can confirm the Radius server is reachable we can ping it from the firewall. There were no changes made on the firewall except upgrad...
We have a site to site VPN tunnel that fails when the vendor side tries to Re-Key. We are seeing no U-Turn policy blocking them. We can ReKey from outside without issue. 1. Has anyone seen this issue previously and been able to fix it? 2. Does anyone have a script that can be run that will logon our firewall and allow me to run 2 commands to ...
Hello Everybody, i thought i try the community for a change with my problem. One of our departments recently asked for a policy change, so their server could access a ressource in the internet. The rule is as simple as it gets. Source is their Server, Destination is a FQDN, Application SSL. (we don't decrypt). We already had a policy which all...
Hello all, It appears that we have had at least a single correlated event in the past seven days, but did not recieve any alert related (via any configured log forwarding profile). It appears the each match that was correlated did perform a log action, but the actual correlated event did not. How do I attach a log forwarding action for Correlate...
I would like to know if anyone has changed HA from AA to AP and has configured floating IP in AA mode. How was the solution to bring it to the AP?Thanks a lot.
Hi all, I understand that GlobalProtect uses TCP 443 and UDP 4501... But what is there any more information available about GlobalProtects usage of port 4501? All I could find is the following: TCP/443 for the SSL communication UDP/4501 for tunnel communication to the GlobalProtect Gateway It doesn't really include much about it.. any ins...
I just need to clarify whether if allowing Web-browsing on a policy would be enough to allow both http(80) and https(443) traffic, ( i.e I don't need to allow both web-browsing and ssl) as it has port 443 as secure port. Thanks
Hello, We are using a PA-220 on version 9.0, its unlicensed, had a real issue getting a new license because the PA-220 was previously purchased off Ebay so we use it now for basic configs now. How do i get the newest firmware for this? I went under devices and then software and hot check now but its not getting me a newer version, I'm stil...
I've seen several posts that asking the same question, but none of them have provided substantial suggestion. Many replies just suggest to use existing templates of Cacti or Zabbix. What if I'm not using those 2 monitoring tools?PA has published an OID list on https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClaSCASHowev...
Hello does anyone know if there is an OID for the session throughput (show session info > throughput)?I would like to monitor that on my firewalls without offloading to get an idea of their load with respect to the max throughput from the tech specs Best regards
Hi all,I'm seeing some odd behaviour with apps that use SQL where the app is on a terminal server. The terminal server has an app installed and works perfectly when the PAN TS agent is not running. When the agent is started, the application throws up lots of connection errors.This happens with multiple terminal servers, multiple app and multiple...
I created a policy (number 21) that allows several types of traffic outbound (ssh, https, tcp 8989, tcp 61000 - 65535, and UDP 1024-65535). All traffic seems to be passing except SSH, which is being blocked by policy number 25, which is supposed to be disabled. During troubleshooting, it looked like policy 25 was responsible for denying my SSH...
| Subject | Likes |
|---|---|
| 5 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 5 | |
| 4 | |
| 3 | |
| 2 | |
| 2 |