dc firewall Management interface
Hi, Where should I connect in terms of security and management if I need to connect to the oob management interface? I have access layer, collapsed core, and server farm switches. Thanks
Greetings, Looking for some assistance in a scenario below; keep in mind I do not have or wish to have SD-WAN 1. ISP1 services the inside and outside connections 2. ISP2 acts as a vpn portal for extenal staff to connect to the inside and route to ISP1 The problem. I would like to force some of my inside servers (mainly backing up to the c...
HiI am using a pair of PA-3250 in HA and have 17 S2S VPNs using my outside interface that has /24 public IP assigned to it. Due to ongoing issues with our current internet, we have decided to move to a different internet platform (DIA) and enhance our redundancy (enable BGP).However, with this new setup, the ISP must give us a new /29 block to e...
Hi All, I was wondering if there is a way to change the font or font size on a Palo device. Couldn't find any relevant doc for it. Thanks, P @BPry @S.Cantwell
I have 2 firewalls in active/passive mode. Am I able to upgrade one of the PAN's and leave the other in standby or passive mode for a few days while I ensure there are no issues before upgrading the second PAN? It is a jump bigger than 2 versions so the PAN I do not upgrade should go into standby mode. Will I be able to then upgrade the device i...
Hello to All, Can the Palo Alto Firewall autoguarantine users based on the number of violations they have made for a particular time? I know that palo alto can add the users or ip addresses to and dynamic group using auto taging with tags (https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-new-features/user-id-features/dynamic-user-groups )...
Entered the credentials, got the push. Gp is showing connecting and after 2 sec showing not connected and minimizes the agent. Exactly after 5 sec agent pops up.. Started spinning and gets connected.(Without asking for credential and push mfa) Version :6.1.0
Hi, i know this is about old software on old hardware, but both are still supported by Palo Alto. In the last months we get a heavy amount of OOM Message / Stack Traces / you name it. Actually we arent able to push new config changes from Panorama to the both devices. Everytime the commit will be aborted by some OOM activities and mostly the M...
Hello all! I hope your day is going well!I wanted to know if Cortex XDR has the availability to filter applications in a report?What my goal is : For example I have 20 systems. Is there any way that I can put a filter on them, to see what Applications those systems have?For example, this is now happening with Groups. I can see what groups are as...
Hello, We have a Panorama premium support and recently trying to create a TAC case and request for engineer on the support portal. But recently we are unable to create one and instead recommend us to use the LIVE community. is there still a way we can create a support ticket and set a call with a TAC engineer? for your advice.
In order to receive the Palo Alto Firewall api keyI checked " curl -k -X GET 'https://<fw-ip>/api/?type=keygen&user=<id>&password=<password>' " in the docsbut where is this command have to enter it? https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-panorama-api/get-started-with-the-pan-os-xml-api/get-your-api-key
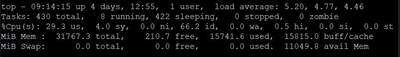
Hello All, I want to ask about memory on PA-850 and PA-3410. i use the calculation "Free Memory/Total Memory = xxx %" and the rest i assume is the used memory but when i see the memory utilization on PA-3410 its only have 210MB for free memory. so when i use the calculation, the free memory only 1% from the total memory, it has a large numb...
hi guys how can I enable mdns forwarding between l3 vlans (my ports are essentially l2 bridges into groups with l3 vlan interfaces having ips and running dchp servers) it seem like bonjur forwarding can only be enabled on physical l3 and not l3 vlans not quite sure what to do thank youalex
Hi all, i wanted to know if there are any issue identified on installing the user-id agent 11.0 on windows server 2022. I have tried it on a server 2022 and there aren't any problem . Wanted to be sure about it and to not have problems in case of a support request. Thanks in advance