General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Pancast: Have an Idea for an Episode?

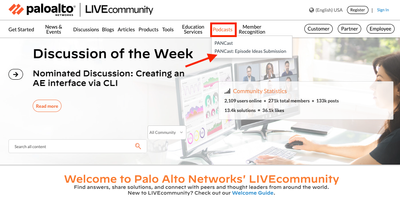
Hey Everyone! Have you listened to the PANCast podcast? PANCast is a Palo Alto Networks podcast that provides actionable insights from cybersecurity experts to customers, helping ensure each day is more secure than the one before it. Since launching last September, PANCast has produced and published 10 episodes — including titles like “Shou...
Screen Shot 2023-02-01 at 7.41.19 AM.png
Screen Shot 2023-02-01 at 7.45.27 AM.png
JayGolf by • Community Team Member
  • 1653 Views
  • 0 replies
  • 0 Likes

Change HA setup A-A to A-P

Good Day. I am looking for pointers wrt changing the HA setup from A-A to A-P mode. The existing setup is for PA-5200s and they are in A-A mode with floating IP bind to active-primary (logically active-passive) and the HA setting is locally managed. Both the FWs are connected to panorama and they have unique interface IPs and dedicated templates...

krlinks by • L0 Member
  • 1704 Views
  • 1 replies
  • 0 Likes

Resolved! Palo Alto integration with Azure Sentinel

Hi All, We are currently working on setting up the Azure Sentinel for our environment and Integration of PA firewalls with Sentinel is our top most priority. However we need to understand what will be the best approach for integration. Should we integrate independent firewalls with Azure Sentinel or Panorama with Azure Sentinel or both firew...

Multiple DHCP scopes on single interface

School network here with an old Windows server running DHCP for our 10 VLANs. Would like to use our PA-3220 firewalls to run DHCP so I can get rid of the old server. Layer 3 routing happens inside the building network on the top of rack switch (Aruba 6405) DHCP Relay is also enabled on the top of rack switch since the DHCP server is on a se...

Resolved! XFF: For security Policy

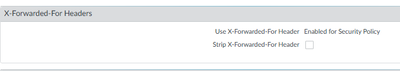
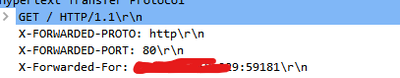
Trying to implement this. https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/policy/identify-users-connected-through-a-proxy-server/use-xff-values-for-ip-based-security-policy-and-logging Azure Web Application Gateway is in the front, acting as proxy. I can see packet captures for port 80 x-forward for is included But i don't see xff in...

image.png
image.png
raji_toor by • L4 Transporter
  • 3425 Views
  • 2 replies
  • 0 Likes

Wildfire on Password protected zip & RAR

Hello experts, How would the Wildfire (submission) on firewall deal with these types 1) password protected zip 2) password protected 7-zip 3) password protected RAR? would it automatically submit by Firewall or need manual submit thru Wildfire portal or API? any ideas? Thanks Harris. WildFire

Resolved! GlobalProtect Portal HTTP redirect

Dear all,We're currently testing the GP VPN solution before we roll it out to our notebooks. We noticed that we can only access the portal homepage if we explicitly enter "https://<portal-url>". It doesn't work with just "<portal-url>" there HTTP would be used. Is there any way to activate an HTTP to HTTPS redirect for the GP portal?...

oschuler by • L4 Transporter
  • 13852 Views
  • 6 replies
  • 1 Likes

Resolved! maximum number of GlobalProtect VPN tunnels for PA-5450

Hello PA community , Our customer is looking for the maximum limit for GlobalProtect Gateways on PA-5450. The most recent KB we found was this which covers 5250, but we would very much like to verify if it is still the same or more for 5450:https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClidCAC we checked also co...

Resolved! IPSEC tunnel

Hi All, Our vendors are migrating their IPSEC tunnel firewall, which is resulting to change the tunnel gateway IP from our palo-alto firewall end as well. So, we are thinking just to create one more ipsec tunnel without tagging the tunnel interface and during maintainace window just to bind the tunnel interface to our new Ipsec tunnel and ...

Sujanya by • L3 Networker
  • 3616 Views
  • 2 replies
  • 0 Likes
  • 24482 Posts
  • 125 Subscriptions
Top Solution Authors
Labels