General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements

Welcome Idira to LIVEcommunity!

Our community just got stronger! Explore new identity security resources, connect with experts, and discover more ways to learn and collaborate.

Meet Idira

General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Audit Global protect server

Hi, We launched a sslab test for a GlobalProtect Portal website. Our note is B. We would like to improve these two things but we dont know what it can be done in PA config. These are: There is no support for secure renegotiation. MORE INFO »This server does not support Forward Secrecy with the reference browsers. Grade capped to B. MORE INFO »...
BigPalo by • L4 Transporter
  • 9365 Views
  • 10 replies
  • 0 Likes

routed-config-p2-failed

Hi All, I am trying to add new interface to the ospf and pushing the configuration from Panorama to firewall, But I am getting the below error while commiting "client routed phase 2 failure", Commit on secondary firewall is succeeding. Issue is only on Primary firewall. When I checked the logs in Palo-Alto firewall, I can see the below:route...

Sujanya by • L3 Networker
  • 2618 Views
  • 1 replies
  • 0 Likes

ACC-SSL Activities

ACC-SSL Activities 'ssl/tlsother'What means? Please note you are posting a public message where community members and experts can provide assistance. Sharing private information such as serial numbers or company information is not recommended.

ZhouYu by • L2 Linker
  • 2047 Views
  • 1 replies
  • 0 Likes

PAN-OS 10.2 on PA-220

Hi All, I was just wondering if anybody had any experience of 10.2 on PA-220 I am thinking of upgrading and haven't heard anything concrete either way. As always thanks in advance for any help.

laurence64 by • L4 Transporter
  • 15039 Views
  • 13 replies
  • 0 Likes

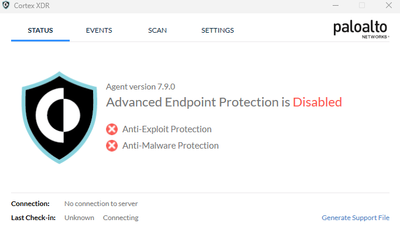
XDR Agent Disabled

I've installed a XDR agent to a workstation, and it's not connecting to the server. I've installed the it on different workstations and that's working fine. After the installation the agent never connected to the server and showing it's disabled. What could be the issue?

Screenshot 2023-01-16 103342.png

panorama scp export more command?

It is linked to equipment A, B, C, D in the panorama. I want to extract only the traffic log for equipment A. ↓ ↓ ↓ ↓ ↓ ↓ The above command extracts all A, B, C, D traffic logs. ↓ ↓ ↓ ↓ ↓ ↓ ↓ scp export log traffic start-time equal 2014/05/16@12:19:02 end-time equal 2014 /05/16@12:19:02 to [email protected]:/home/goran/kb1.csv Can't ...

qmso475 by • L3 Networker
  • 1616 Views
  • 1 replies
  • 0 Likes

[ICMP Covert Channel] Allow only ICMP Ping packet that has specific payload.

Dear all, I am using PA-8.0.0-ESXi virtual machine and I am trying to prevent covert channel communication using ICMP Payload. For example, as captured using Wireshark, the default ICMP type 8 (Echo request) for Windows machine is abcdefghijklmnopqrstuvwabcdefghi or \x 61 62 63 64 65 66 67 68 69 6a 6b 6c 6d 6e 6f 70 71 72 73 74 75 76 77 61 62 63...

hibagus by • L2 Linker
  • 16001 Views
  • 15 replies
  • 1 Likes

block IP's in same zone

Is it possible or practical to block traffic between two server in the same firewall zone by designating the source IP from the server you want to block access to the server to the destination server indicated by IP

jdprovine by • L4 Transporter
  • 19054 Views
  • 35 replies
  • 0 Likes

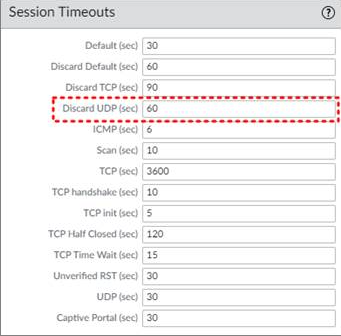
Discard UDP from Paloalto Session TImeout

  Hello all,Recently, customers are experiencing a phenomenon that Syslog traffic coming into the same source port remains in the Discarded Deny Session. As a result of my checking, it was confirmed that it occurred while being constantly refreshed due to Discard UDP Timeout in Paloalto Session Timeout setting.Discard UDP : Maximum length of tim...

Screenshot 2023-01-12 at 9.40.17 AM.png

PA440 not booting

Hi everyone, I have a problem after rebooting a PA440. The device simply puts a message on the console that no bootable media has been found and then shows a BIOS-like menu with several entries (boot manager, system setup etc.). However, if I select one of these entries, it asks me for a password - neither the serial number, MA1NT, admin nor the...

ad_hoe by • L0 Member
  • 9482 Views
  • 3 replies
  • 0 Likes

Resolved! Listed amount & type memory for PA-850

Maybe I am missing something but my security group requires the memory amount and type used for hardware devices prior to admittance on classified networks. I don't see a confirmed type and amount in any of the documentation. Was wondering if this was available?

J.Luce by • L0 Member
  • 2866 Views
  • 2 replies
  • 0 Likes

Allowed sites not loading correctly

I am new to Palo Alto Firewalls so I am trying to figure this out. In our policy we have facebook allowed and it is not displaying the whole page. Am I missing something? Please note you are posting a public message where community members and experts can provide assistance. Sharing private information such as serial numbers or company informati...

  • 24484 Posts
  • 125 Subscriptions
Top Solution Authors
Labels