This website uses Cookies. By clicking Accept, you agree to the storing of cookies on your device to enhance your community and translation experience. Read our Privacy Policy.
Click Preferences to customize your cookie settings.






Slowness when filtering at destination in a rule by address-group
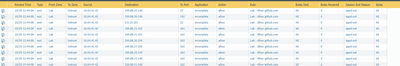
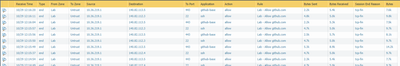
Hi, We are having slowness in a traffic when the destination in the security rule is a address-group. If we configure "any" in destination the session are fast. The traffic is 443 (web-browsing). How PA can cause slowness in https if the destination is a address-group? any idea?


 Raido_Rattameis