General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Internet speedtest from PAN

Is it at all possible to determine circuit capacity directly from the PAN?Esentially what im trying to do is run a intenret speedtest directly from a PAN.What would be perfect is the ability to run an iperf client direclty off a PAN
ivan01 by • L0 Member
  • 14386 Views
  • 2 replies
  • 2 Likes

Resolved! Routing issue with Palo alto

Hello everyone!I am experiencing an odd problem.I have 3250 HA pairs. I have configured 2 aggregate(L3 trunk) interfaces and added sub interfaces to these aggregate.The first problem is the firewall itself can not ping directly connected device by using "ping source x.x.x.x host y.y.y.y" command.Every sub interface has management profile assigne...

ESXI Server & Palo Alto: The Inside Hosts that's on the same port Group as Palo Alto (inside interface) cant ping the Palo Alto inside Interface.

I have a ESXI Server with firewall (Inside, DMZ and Outside) zonesPalo Alto has a security rule to allow interzone traffic from inside to outsidePalo Alto has NAT configured for Outside Interface When I try to ping from host to host on in the same port group...all is good.When I try to ping from host to the Inside Firewall Interface, the ping ti...

ETate by • L1 Bithead
  • 2221 Views
  • 1 replies
  • 0 Likes

Unable to ping out from new zone

We are in the process of migrating our DMZ servers out from behind an ancient ASA to our Palo. I pulled a test webserver over to make sure my NAT was set and to trial out some rules.For the most part everything is working but I can't ping out from a server in our DMZ zone. We are using GlobalProtect for our VPN and from the vpn zone I can ping t...

Evahi21 by • L0 Member
  • 3209 Views
  • 1 replies
  • 0 Likes

Resolved! How to Block Community Member

How can I block community member repeatedly posting questions on https://live.paloaltonetworks.com/t5/customer-resources/support-pan-os-software-release-guidance/tac-p/441609#M523?

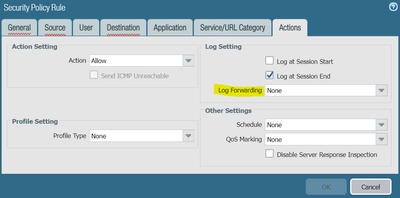
Resolved! Security Policy Rule Actions Tab

Hello -For various reasons we no longer use "default" for log forwarding as a log forwarding profile and actually delete it and have a new one, let's call it Log_Forward. When a new rule is created, if default is still present, it will autofill the Actions tab > Log Setting > Log Forwarding with default. If, as in my case, we don't have d...

RobertShawver_0-1634317988460.png

Management SSH port not accessible

Hi Team, We have FIX WEAK CIPHERS AND KEYS ON THE MANAGEMENT INTERFACE FOR SSH ACCESS with help of the below document.https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000PN5bCAG As of now, we are not able to access the firewall management SSH access. we required FW mgmt SSH access. Firewall in HA MODE, the secondary firewal...

VishnuPS by • L3 Networker
  • 3306 Views
  • 1 replies
  • 0 Likes

Resolved! Captive portal problem

Hello,I have configured the Captive portal but i am not able to open the web page.PAN-OS version- 9.0.9Below is my configuration:-1 - LDAP authentication2 - Configured interface management profile with the check response page.3 - enabled user identification.4 - configured authentication policy.5 - Apply forward proxy decryption. After some troub...

how to integrate paloalto firewall with Cortex XSOAR

Hi, I have setup Cortex XSOAR. However, i'm still confuse what i can do with this platform.. Someone said, i can integrate my Paloalto Firewall with Cortex XSOAR... Is there anyone here, know how to integrate my Palo alto firewall with Cortex XSOAR?

HA configuration back to a Cisco Nexus switch, question about port-channels

Our current environment has two PA-850s connecting to two Cisco Nexus switches. Each PA-850 has a fiber connection to each Nexus. The Nexus has a configuration of a single port-channel covering all four fiber links. Is this how it should be done, or should I have a port-channel for PA-3220 (1) and another port-channel for PA-3220 (2)? Current...

Resolved! Is Panoroma(all model, vm) logging disk use RAID technology

Hi All,I am curious to know which technology is using in Panoroma logging disk to store the logs or disaster recovery. I have added 6TB virtual disk in panoroma now it is showing DiskA, DiskB, DiskC,DiskD, DiskE. If any one Disk get faulty how data will get from the faulty disk.

Resolved! Question about moving traffic to new rule

Hello Palo Alto Community, I have a question regarding moving https traffic off a rule to another existing rule. The traffic being moved is critical to operations and cannot be disrupted. For this reason I've been asked to confirm the behaviour of this change. I don't see any issues with proceeding however would like to confirm the impact. My th...

PA_User by • L0 Member
  • 2865 Views
  • 2 replies
  • 0 Likes

Impact on Processing rulebase order

Hi,Is there and if so what is the difference on processing speed of a PA rulebase when most hit rules are on top vs when most hit rules are spread throughout the rule base?For example: Imagine a rulebase of 15000 rules. What would be the processing speed difference if a certain rule is hit 10000 times a day if it's on top (say 1th rule in the ru...

  • 24463 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels



