Does Palo Alto Networks Support actually exist?
Nobody will answer their phones. Several attempts to call support only leads to hours on hold, nobody ever answers.

It is my understanding that I should be able to export my config on the primary PA-850 and import it to the primary PA-3220. I know that there are more RJ45 ethernet ports on the PA-3220, so I will update Ethernet1/9 to Ethernet1/13 and Ethernet1/10 to Ethernet1/14. I am also planning on using the HSCI port for HA, so I will need to update HA1...
I am sure this is going to be something simple, but I am admittedly stumped (not hard to do). I have a block of External IP addresses assigned by our ISP , say 172.10.10.10/29 The gateway is 172.10.10.10 . This contains a single physical port . This is connected to a switch to allow distribution of multiple ports. I have 2 firewalls attached....
Push to devices failed after upgrade to 10.0.6, we currenty try to push a change on Panorama for a pair of firewallsrunning all 10.0.6 , the commit to panorama went well , but after choice the specific device group and template stack we clicked validate to device group and this showed failed, the same for validate for template, we push anyway an...
Is it at all possible to determine circuit capacity directly from the PAN?Esentially what im trying to do is run a intenret speedtest directly from a PAN.What would be perfect is the ability to run an iperf client direclty off a PAN
Hello everyone!I am experiencing an odd problem.I have 3250 HA pairs. I have configured 2 aggregate(L3 trunk) interfaces and added sub interfaces to these aggregate.The first problem is the firewall itself can not ping directly connected device by using "ping source x.x.x.x host y.y.y.y" command.Every sub interface has management profile assigne...
I have a ESXI Server with firewall (Inside, DMZ and Outside) zonesPalo Alto has a security rule to allow interzone traffic from inside to outsidePalo Alto has NAT configured for Outside Interface When I try to ping from host to host on in the same port group...all is good.When I try to ping from host to the Inside Firewall Interface, the ping ti...
We are in the process of migrating our DMZ servers out from behind an ancient ASA to our Palo. I pulled a test webserver over to make sure my NAT was set and to trial out some rules.For the most part everything is working but I can't ping out from a server in our DMZ zone. We are using GlobalProtect for our VPN and from the vpn zone I can ping t...
How can I block community member repeatedly posting questions on https://live.paloaltonetworks.com/t5/customer-resources/support-pan-os-software-release-guidance/tac-p/441609#M523?
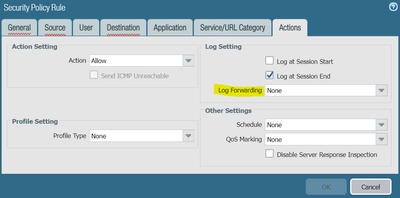
Hello -For various reasons we no longer use "default" for log forwarding as a log forwarding profile and actually delete it and have a new one, let's call it Log_Forward. When a new rule is created, if default is still present, it will autofill the Actions tab > Log Setting > Log Forwarding with default. If, as in my case, we don't have d...
I have applied threat id exception on antivirus profile, can i get the logs for those id in threat logs.
Hi Team, We have FIX WEAK CIPHERS AND KEYS ON THE MANAGEMENT INTERFACE FOR SSH ACCESS with help of the below document.https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000PN5bCAG As of now, we are not able to access the firewall management SSH access. we required FW mgmt SSH access. Firewall in HA MODE, the secondary firewal...
Hello,I have configured the Captive portal but i am not able to open the web page.PAN-OS version- 9.0.9Below is my configuration:-1 - LDAP authentication2 - Configured interface management profile with the check response page.3 - enabled user identification.4 - configured authentication policy.5 - Apply forward proxy decryption. After some troub...
Hi, I have setup Cortex XSOAR. However, i'm still confuse what i can do with this platform.. Someone said, i can integrate my Paloalto Firewall with Cortex XSOAR... Is there anyone here, know how to integrate my Palo alto firewall with Cortex XSOAR?
Our current environment has two PA-850s connecting to two Cisco Nexus switches. Each PA-850 has a fiber connection to each Nexus. The Nexus has a configuration of a single port-channel covering all four fiber links. Is this how it should be done, or should I have a port-channel for PA-3220 (1) and another port-channel for PA-3220 (2)? Current...
| Subject | Likes |
|---|---|
| 5 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 5 | |
| 4 | |
| 3 | |
| 2 | |
| 2 |





