General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

10.0 user-id agent ignore_user_list not working

Since upgrading to pan os 10.0.6, we've noticed the "ignore_user_list" on our server user-id agents doesn't seem to be working. We did not have any issues prior to upgrading to 10.0.x. Has anyone else noticed this issue? We upgraded our user-id agent to 10.0.3-10 (latest version) at the same time. We have a support ticket open, but have yet ...
jmurphy by • L2 Linker
  • 2605 Views
  • 1 replies
  • 0 Likes

Http traffic to https

Hi Guys Can we redirect someone trying to access http://www.xxx.com to https://www.xxx.com ( port 80 to 443 ) ?If we are using Dest NAT for https://www.xxx.com ? Thanks

i_maddy by • L0 Member
  • 2540 Views
  • 1 replies
  • 0 Likes

Resolved! Assign multiple netflow profile to an interface

Hi AllWe have multiple netflow servers in the environment and i want to configure palo alto firewall interface with multiple netflow server profiles. I have already one netflow server profile attached to my Layer3 interfaces and now i want to configure another netflow server profile and attach to these interface but don't know how to do it. Is i...

Resolved! GlobalProtect uninstall problem

Hi,Our user have a problem with GlobalProtect client on a computer running Windows 8. Client was behaving very unpredictable (constantly connecting and disconnecting from the VPN), so it is uninstalled (from Control Panel\Programs\Programs and Features - Uninstall a program).Now, when attempting to install the new GP client he getsHe rebooted th...

Decrypt GlobalProtect traffic

Hi Guys!I have a GlobalProtect (IPSec) configuration with an external gateway, all remote user traffic goes through the vpn tunnel, to which I apply decrypt policies for this traffic.The problem is that in applications like "teams", it is not possible to share screen, send messages, etc. while connected to GP.When I disable the Decrypt rules, ev...

PA-220 Thermal Shutdown

Morning All, Here in the UK, we are in the midst of a heatwave and we have had 2 PA-220's shutdown for heat issues. I can't find anywhere at what temperature the Palo shutdown due to temps? I thought it was the MAX Chasis temp, however, we have another Palo that's passed the MAX of 60c and not shutdown. Has anyone got any info or experience? Tha...

Guide for mp-log and dp-log troubleshooting

Hi All, Is there a comprehensive guide for knowing which logs to look at in the mp-log and dp-log eg. what log files to look when troubleshooting a particular issue on. For example if im troubleshooting some OSPF issue, i can look at the mp-log routed.log or for lacp it would be the l2ctrld.log.

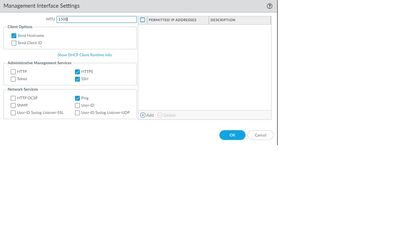
Settings missing in Management Interface

I cannot see any option to change any Management Interface settings under Device > Setup > Interface.>show system info is showing ip-assignment: dhcp. I need to change it to Static.I have tried the commands below but no change.> configure# set deviceconfig system type static# commitInvalid configuration. Please fix errors and try aga...

Interface Settings.jpg

Bi-Directional NAT To External IP not Configured on an Interface

Hey All,Working on a PA-220 on 10.0.6 here. I am trying to configure a BI-DI NAT for inside Zone A host 10.0.0.4 to Zone B public IP: 5.183.105.227. This traffic is to allow a vendor to build an IPSec VPN tunnel between their VPN appliance configured as 10.0.0.4 to their remote peer VPN of 99.169.208.245. Zone A = Inside (Interface 1/6: 10.0.0.1...

Traffic block due to EDL

I have found traffic blocked due to edl inbound policy. Traffic is blocked for random time like hour or one and half hours for random port.after some time traffic is moving. Another thing is traffic is moving for one destination ip and this destination ip is not in that edl list, but traffic blocked and move in random time for this destination. ...

SurajN by • L2 Linker
  • 2487 Views
  • 1 replies
  • 0 Likes

PA 410 reboot time

Anyone know the reboot time on a PA 410? Looking to see if its better than the PA 220. Thank you,Ted

treese by • L3 Networker
  • 3673 Views
  • 2 replies
  • 0 Likes

Resolved! Required permissions for Active Directory integration

Hello, I am trying to get AD authentication to work for GlobalProtect. I have been following this document https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000CmAdCAK for configuring the AD integration part, and it says: Before you integrate a Palo Alto Networks device with AD, you must create a user ID in AD that you'll u...

client certificate authentication fails even though machine has certificate.

One of my setup with client certificate authentication in gateway was working fine. For some reason, it gives me 'Required client certificate not found. Please contact your IT administrator' error. The certificate is available in the client machine certificate store and PanGPS.log shows it is able to identify the same. But After which it fails a...

Resolved! Is there a better way to block non-default app ports?

After parsing some logging I've discovered some trends in users utilizing non-standard ports for some App IDs and I want to prevent that. The first thing that comes to mind if to create a policy only allowing the app-default port, but the issue is currently this traffic is hitting a more general permit rule at the bottom of the policy stack. We ...

  • 24463 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels