General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

SSO authentication was solved through override, cause analysis request and Similars

Hi. I have a website that I access via sso authentication, but I can't connect through the firewall. After trying various things, I solved it through the override rule in the firewall The override policy cannot be removed at this time. I wonder why this is possible with an override. Does anyone have a similar case or guess? Tell me please.
jskang by • L1 Bithead
  • 2626 Views
  • 1 replies
  • 0 Likes

Resolved! Captive Portal LDAP Authentication redundancy

Hello. I have a Captive Portal that uses next Authentication Profile:CP_AuthWhere:Authentication Sequence:CP_Auth - Auth_Mode_1, Auth_Mode_2Authentication Profile:Auth_Mode_1 - LDAP_1Auth_Mode_2 - LDAP_2LDAP Server Profile:LDAP_1: 10.10.1.101, 10.10.1.102LDAP_2: 10.10.2.103, 10.10.2.104 Base on our monitor logs, we noticed that all our authentic...

JuanAn by • L1 Bithead
  • 5970 Views
  • 4 replies
  • 0 Likes

Resolved! Panorama IPsec tunnel to AWS

Need to create IPSec tunnel in Panorama hosted in Google Cloud that is managing our PAN-850 in customer datacenter to our cloud environment in AWS. FYI-we dont have Palo Alto in AWS.

Resolved! unsigned LDAP

Hi,As we know Microsoft is going to disable use of unsigned LDAP port 389 in March 2020.Fortunately I don't have LDAP profile on my PA firewall but I have Kerberos. Will there be any impact ? and do I have to change it ? Thank youKonrad

Resolved! CLI command for IPSEC tunnel info

Hello friends, I am looking for cli command to see all the details related to ipsec tunnels configured on the gateway. I need information related to tunnel id, peer ip and their status. Is there any command available ? I can see details under gui but i cant see tunnel id. Please help on this. Thank you.

Joshim by • L1 Bithead
  • 50413 Views
  • 4 replies
  • 0 Likes

SSL test pages of urlfiltering.paloaltonetworks.com not blocked

Hi,If we test https://urlfiltering.paloaltonetworks.com/test-grayware there is no block page however if we test http://urlfiltering.paloaltonetworks.com/test-grayware we do get a block page. I cannot find urlfiltering.paloaltonetworks.com nor *.paloaltonetworks.com in a no ssl decryption profile nor the predefined exclusion list.In the traffic l...

tomdevos by • L0 Member
  • 3479 Views
  • 1 replies
  • 0 Likes

Route between Subinterfaces with two VRs

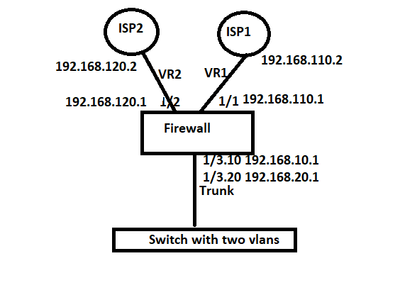
Hello, I have a network with two WAN connections, i have assigned one of them for a vlan 10 and the other for vlan 20 using two VR and NATing also i created dhcp server for both vlan and for now every thing works fine, the problem is i can't access the resources in vlan 20 from vlan 10 and vise versa, what should i do also? should i create a sta...

Untitled.png

How to remove one BGP-RIB Out

Hi, We've configured BGP between Paloalto to Azure by using EBGP. The bgp is established but in RIB Out noticed that prefix 0.0.0.0/0 advertised to the peer respective azure. How to remove this, because due to this the users in bgp unable to access the internet. If I enable the "reject default route" option does this help? or cause any problem ...

bgp azure.JPG
bgp azure.JPG
bgp azure.JPG

RADIUS Authentication Still Prompts for Password Change

I have a stand-alone system which is utilizing two Palo Alto 220 Firewalls. As part of this system, I have RADIUS policies configured on a Windows server to provide domain-admin access to the device. On one PA220 I am able to login with my domain credentials and access the device without issue. On the other PA220 I am able to login with domain c...

TAP Mode

Hi, I want to know if there is a way to forward all switch traffic to single Destination port of Palo alto. So far I can find on switch side you can make a singel port source and destination the PA port. Just want to know if we can monitor all ports on the switch? Thanks

umar00o by • L2 Linker
  • 3688 Views
  • 3 replies
  • 0 Likes

Shared Gateway and Panorama

Hello Community,I have Panorama that managed cluster of PA-5000 with some Virtual System, I use one Device Group for one VSYS.Now I need to configure the Shared Gateway.It seems that i can manage the NAT Policy related to the Shared Group only into WebUI of device and not from Panorama.Could you confirm me I cannot managed it via Panorama? Thank...

Run operational command using SSH

I need to automate run particular operational commands , which were not available in the API. I tried running them using SSH to the Panorama CLI, but it fails. Also Paramiko Python script does not seem to work and not sure what are we doing wrong. Can you please share any experience exectuing SSH commands?

batd2 by • L4 Transporter
  • 6179 Views
  • 3 replies
  • 0 Likes

Statistics for data transfer on a Palo Alto.

Team,I am looking to gather some reports which will tell me how much traffic has been passed over a specific VPN tunnel on a Palo Alto.Is that possible?The preferred stats are over a month or a 15 day period. If yes, can you guide me on how can I create these reports? Thanks!!!

nson2139 by • L3 Networker
  • 3536 Views
  • 1 replies
  • 0 Likes

unable to reach peer end public IP via vpn tunnel

HI Team I have created S2S VPN tunnel between palo alto and cyberoam firewall. Tunnel is up but the traffic is not flow. Under Cyberoam firewall there is one server with public IP 144.21.X.X.From palo alto we need to reach the peer end public IP 144.21.X.X via the vpn tunnel.but whenever I tried to reach the peer end public IP 144.21.X.X its go...

  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





