General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Knowledge sharing: High Data Plane CPU because of DDOS or overutilization (access to Palo Alto Auto Assistant may help)

I have seen for example on a small firewall when the customer enables SSL decryption that the counters for work groups "ecdhe_key_gen", "flow_host " etc. jump. This may show that the firewall can't handle the ssl decryption or that there is an SSL DDOS attack: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000CmV2CAK ht...

behavior in multi-vsys with shared gateway and DNAT policies

Dear community, We have a firewall with multi-vsys and the following scenario: 1 shared gateway and 1 public IP on external zone 1 virtual system and 1 private IP on internal zone We configured DNAT to allow access to private IP from Internet following this article:https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClHxCAK...

Carracido by • L4 Transporter
  • 3627 Views
  • 3 replies
  • 0 Likes

Resolved! Traffic Thourhg the intended Security Rule

Hello, I have configured a new Security Rule on top (#9 in the picture down) to Block traffic intended to a Custom URL configured in the profile Block_Files* TOP RULE *Source Zone: anySource Address: anyDestination Zone: anyDestination Address: any * NEXT RULE *Source Zone: Trus...

mshamsan by • L1 Bithead
  • 4224 Views
  • 3 replies
  • 0 Likes

HA Active/Passive with Preemption

2 firewalls configured with HA active/passive, And enabled preempt on both of firewallsEverythings find, can synchronize configuration and session firewall-A is active-firewall with priority 100firewall-B is passive-firewall with priority 120HA timer settings is recommended But when I was testing for HA switch over by unplugged a interface on Ac...

Difference between last 24 hour and last calendar date option in reports

Hi All, What is the difference between last 24 hours and last calendar day time frame option that is being used in custom report settings. Also last 24 hours time frame means past 24 hours data will be added to the report the minute report is run. But how does it works for last calendar day. Thanks in advance. Re: Custom Reports contained in Gr...

IKE SA negotiation is started as initiator, non-rekey

Hello :),I have a problem with VPN from PA-220 to Azure. The logs show this information : "IKEv2 IKE SA negotiation is started as initiator, non-rekey. Initiated SA " Every change I made it always is this same error. Is there any way to resolve this issue ? Thanks in advance 🙂

Lukaszm1 by • L1 Bithead
  • 56545 Views
  • 9 replies
  • 0 Likes

System Logs

Hi, Do we have any list of critical and high severity system logs? Like what are the examples of hardware failures, serious issues etc...

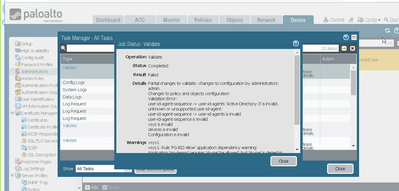
user-id-agent-sequence is invalid.

Hi Team, I'm seeing configuration invalid when I remove user-id agent from palo alto firewall and not able to commit. PA-220 PANOS version 8.0.3. Same model firewall I have removed I can able to commit. Only in this firewall, I'm seeing this issue.

Screenshot (500).png

Total number of profiles

Hi, We have the problem with the total number of security profiles.As you can see in attached screenshot the maximum number of profiles is 100, for now we have 84, but when I tried to add new one I get the capacity error. Maybe someone had the same problem.Model - PA-820

Resolved! Packet Flow Query - FW Inspection

Hi Everyone, I've been madly studying the Packet Flow Diagram that outlines the different checks/stages that a Packet goes through via a PA FW and I had a question with the 3rd check in the Ingress phase called 'FW Inspection applicable'. If Inspection is applicable then it carries into the IPSec/SSL VPN tunnel check but if Inspection is not app...

Resolved! implement the PA External Dynamic List (EDL) IP/Domain blocklists

Hello, we have an existing opened case PA case (01865541) but having trouble and delays in getting connected with PA engr. Hence, am trying my luck here in Live community. My customer is preparing to implement the PA External Dynamic List (EDL) IP/Domain blocklists on our PA, but it is not able to retrieve the EDL from server URL. QUESTIONS:...

User ID and AD

Hi,I am trying to configure User ID with Active Directory. But stuck with some errors, listed below :1) Unable to retrieve the Userid IP mapping information from Active Directory (win 2003 Sp2).2) After installing the User ID Agent and configuring... when i click the commit button in User-ID Agent the Agent is not responding and hanging. (In Wi...

Resolved! VPN CLIENT GLOBAL PROTECT, MANAGED WITH LDAP GROUPS

Hello, I have a problem.I just inherited a palo alto firewall.I noticed that given a specific certificate and given the global protect client, every user of the ldap server can connect to the vpn.I would like that only users in specific ldap groups could enter.Let's say the groups come from active directory."domain"\user_group_allowed"domain"\us...

No Source User

After the .NET/User ID agent issue last week we upgraded the agents and managed to get our UserID mapping back so our firewall policies would work again. At this point I have user > IP mapping, all of my agents are connected and my user based firewall policies are working. The issue we see now is even though UserID is working the firewalls ar...

mmeehan by • L2 Linker
  • 3314 Views
  • 2 replies
  • 0 Likes

Resolved! Global Protect pre-logon and user IP Pools

I'm wondering if anyone can help. We have global protect setup and i want to use the same IP Pool for pre-logon user's, and once authenticated have that same IP pool used for the user. So when i am setting this up in the client settings area of the Global Protect gateway area, i would like to add a pre-logon profile with a pool, then add the use...

  • 24482 Posts
  • 125 Subscriptions
Top Solution Authors
Labels




