How to allow policy destination by URL
Hello, I need know how to allow create policy in PA firewall 3020 and add destination as URL name as (microsoft office 365) instead of adding all IP ranges. Appreciate your help Thanks
Hi Team, we have two isp link with ecmp load-balancing enabled. we only have one virtual router setup. we have configured GP vpn portal with one isp interface and how can i configure the GP vpn with second isp link as well. we would like to have two external Gateway.But global protect portal only showing to choose one outgoing interface.any help?
Hi All, I understand that this is a Microsoft related matter however I'm interested to see if anyone else has come across this issue. With Global Protect Network Enforcement in place (through the Portal Config), it is still possible for local admins to end the 'GlobalProtect service' (PanGPS.exe) Windows Task and bypass the connection enforcemen...
Hello All, Do any of you compare local firewall or Panorama configurations against CIS benchmarks for security compliance checks ?Either using an existing tool to check Firewall compliance with the CIS (Centre for Internet Security benchmarks) recommendations or manually using show merged config / show config ? The Palo BPA does expose some of t...
Hello. AD integration using the User-ID agent. We were on 8.0.7-2 and things were working fine. I tried upgrading to version 8.1.0-66 and had several problems with wrong user-id being reported. I saw in the release notes for 8.1:• Since multiple username attributes are supported, you must select the PrimaryUsername attribute that you want to u...
Hello, We enabled a week ago the feature enforce network access on our environment.We are using internal host resolution to detect if user is inside or outside corporate network.In a random way, we're experiencing issue with users worldwide. We have a dns server at each location This issue seems to be present only when the user is connected from...
https://applipedia.paloaltonetworks.com/ is not working as of 06/17/2021 3:05 MDT
Hi, Is there any way to block this psiphon app? is it needed ssldecrypt?This app uses many apps (ike,ssh,ssl) so we can not block them. How do you block this app psiphon?
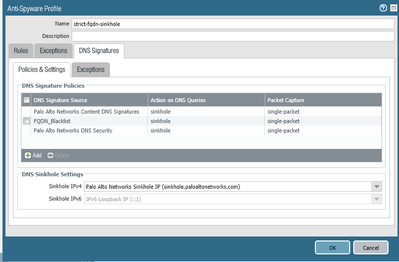
I'm trying to figure out wh my Dns Sinkhole Adoption Rate fell to 77% from 100% over the past six months. Every security policy is using the same anti-spyware policy. Any ideas?
Across a large environment, what would be the best way to audit Palo administrator accounts? That is accounts found at Device > Administrators. For various reasons we all end up with lots of AD accounts, service accounts and so on there, what I'd like to do is find a way to periodically check those accounts against AD to see if they are stil...
Hi Guys, I noticed some strange logs on one of our 5200 firewalls.There is device behind the firewall that is running constant ping to google dns, traffic is allowed and working normally.I noticed a some logs that bytes sent is zero... I can explain bytes received with no reply, but I don't have any explanation why log entry will have bytes sent...
Black PsiphonDear All, Psiphon was blocked for a long time but this week, we detect it has been working again. i have tried to block it again but without any result, it was blocked for 2 hours and working again after that. I have been checking the traffic monitor and found Psiphon used (any category), and used telnet, SSL, https, https, etc to g...
Am trying to create an app id that identifies a particular pattern that only be 10 characters long and must be alphanumeric, had tried various syntax but seems not to be accepted as a correct pattern with the message that the expression is not at least 7 bytes. Anyone whom have such experiences can share the the correct expression syntax? Thank...
Is there a way to split a large output feed into smaller feeds.
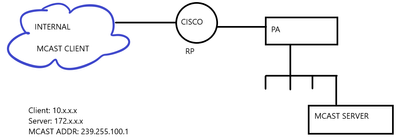
I have tested multicast to be working and is configured as in this diagram. In the logs I see traffic from SERVER zone to Multicast zone. But there is no log on INTERNAL client that accessed the multicast stream.
| Subject | Likes |
|---|---|
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like | |
| 1 Like |