General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! GlobalProtect clients experiencing latency delays

Hello, Clients who are connected via GlobalProtect VPN are experiencing slowness with all their traffic traversing the VPN (ie.. Internet and Server access traffic).The latency is between 200-400ms for all the traffic regardless of whether its Internet based (to google) or server based (to our corporate servers). Can you suggest any troubleshoot...

Farzana by • L4 Transporter
  • 16879 Views
  • 12 replies
  • 0 Likes

Resolved! GlobalProtect Gateway: can it share an IP used in NAT/Security Policies?

I have a working GlobalProtect setup right now using a single Portal on the district firewall, and a single Gateway on the firewall for the location I want to have access to. Currently, these are using dedicated public IPs that are not used for anything else, assigned to the public interface of the two firewalls. What I can't figure out from sea...

fjwcash by • L4 Transporter
  • 12492 Views
  • 9 replies
  • 0 Likes

AE Interface down during failover

We recently had a failover event during a normal upgrade of the firewall (10.0.1 -> 10.0.4). The LACP aggregate interface on the Cisco switch / Firewall did not come up during this time, which resulted in a longer than expected outage. Powered down firewall to restore original firewall connection. We are using Active/Passive pair with PA-820....

Service route in panorama.

Dear Team, I have two interfaces configured in my panorama:1-management interface2 -ethernet1/1. for software and dynamic updates by default, my traffic is going via management interface. I want to change the service route through ethernet1/1 but I am not able to see any option to change the service route. below is the snapshot. can anyone help ...

Jafar_Hussain_0-1593346305511.png

Resolved! Study tip for PCNSA.

Hello everyone, I spent a year working directly with Palo Alto firewall and I would like to get some certifications, but all video content I find is purely in English and I still don't have a command of the language. Did they have any text material tips to aid in the study? Any tips to add would also help a lot. Thanks!

Amaro123 by • L2 Linker
  • 5380 Views
  • 2 replies
  • 1 Likes

Resolved! Policy Based Forwarding

Hi All, I have a guest wifi vlan 10.25.x.x that needs to be routed out to a second ISP. AP-->WLC--Palo Alto FW-->MPLS/VPLS-Router-->L3Switch-->ISP The vlan will each have a sub-interface and gateway 10.25.x.1 assigned on firewall in its own guest zone and virtual router. The virtual router will have a default gateway 0.0.0.0 to a ...

MistryJa by • L1 Bithead
  • 3927 Views
  • 2 replies
  • 0 Likes

OKTA SAML panorama authentication?

Trying to get this working and I am able to authenticate using OKTA SAML via the button on the login screen but when I do (after entering u/p on the OKTA page) it redirects me back to the Panorama login page. I see PAN_AUTH_SCUESS SAML on the CLI but never an 'auth-sucess' in the GUI (Monitor > Logs ? System) because it never actually logs ...

drewdown by • L4 Transporter
  • 7128 Views
  • 5 replies
  • 0 Likes

Resolved! 1:1 destination nat mapping

Hi everybody, does anybody know if it is possible to write a single destination NAT policy in order to map ip addresses from a given range/network to a corresponding range/network of the same size preserving the host portion of the address? I try to explain with an example. I would like to translate packets destined to 192.168.10.0/24 with add...

grenzi by • L3 Networker
  • 6534 Views
  • 3 replies
  • 0 Likes

Custom Snort Signature

creating a custom snort signature on Palo alto Firewall but didn’t found the concern context operator for match pattern.Shall we create a context operator or how it can add the pattern if the context operator is not available? For example:alert tcp $HOME_NET any -> $EXTERNAL_NET 443 (msg:"[CIS] Emotet C2 Traffic Using Form Data to Send Passwo...

Snort.jpg

Resolved! Global Protect Split Tunnelling

We are enabling split tunnelling for O365 traffic. I have added a object for a known website so I can test this. I can see the IPs in the PANGPS logs so the configuration is pushed to the client. I have also enabled the Split Tunnelling in the APP for Network and DNS. When I am connected to Global Protect and visit the test website it is incredi...

a.jones by • L3 Networker
  • 3737 Views
  • 2 replies
  • 0 Likes

TS Agent - System Source Port Allocation Range Registry Key

Hey, the following text you can find on this page:The System Source Port Allocation Range and System Reserved Source Ports fields specify the range of ports that will be allocated to non-user sessions. Make sure the values specified in these fields do not overlap with the ports you designate for user traffic. These values can only be changed by ...

J.Schoen by • L0 Member
  • 8294 Views
  • 3 replies
  • 0 Likes

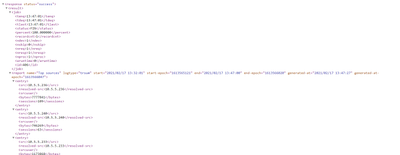
Unable to export ACC last-60-seconds stats

Hi,I'm looking for a way to export regular per-IP bandwidth usage stats in a human-readable format. I have found out that it's possible to get this in .xml via REST API. I'm trying to create a top-src-summary for the period of last-60-seconds. This however generates a blank report (see the first screenshot). There is no issue, if I generate a re...

Capture1.PNG
Capture2.PNG
DuzyGl by • L0 Member
  • 2899 Views
  • 3 replies
  • 0 Likes

Resolved! Global Protect Always On and stopping local network access in event of failure

Hi All, Is it possible to stop a device from connecting to the local network if the Global Protect Gateway fails? I have a question from a customer that has an Always On Pre-Logon environment and wants to ensure the connection defaults to a fail-closed mode with no access to the local netwok - although it must allow for initial connections to ne...

a.jones by • L3 Networker
  • 3228 Views
  • 2 replies
  • 0 Likes
  • 24464 Posts
  • 125 Subscriptions
Top Solution Authors
Top Liked Authors
Labels