Protocol Confirmation Required for Industrial Firewalls IEEE C37.94
Can somebody confrim if palo alo firewalls supports these protocols "IEEE C37.94 or not need solid answer for industrial firewalls???
Hi, I am a newbie for PA and need of some assistance in configuring PA VM on OCI. I have done the basic configuration Created Zones and Virtual routes etc. I need to create a IPSec VPN from OCI PA VM to OCI VPN (Not a PA VM) setup on a another tenancy. Both configuration identical except for IP address. Added rules to allow all and a NAT tow...
Hello Team, Need help to set up an IPv6 for VM series NGFW which is hosted in AWS env. We are able to see the IPV6 traffic on NGFW, getting Aged out logs for the IPV6 traffic. rules are present in NGFW to process the IPV6 traffic.
Hello, I am the user mentioned in the title. My email address is email@domain, and I am using it through Outlook. I am able to receive emails such as release notes and update notifications for various content without issues. However, I am unable to receive emails that I am directly referenced on for cases, and these messages are not being cate...
Hi Can you help me with US ECCN for PA-5410 please?
Dear LIVEcommunity Members, Ensuring a top-tier experience on LIVEcommunity and protecting our members’ safety and security is our top priority! To this end, we have implemented additional security measures to safeguard our vibrant global community. We also want to take this opportunity to remind members that they have the authority to repo...
Hi, After my Palo account manager encouraged me to use the AI-Ops page, I uploaded the most recent techsupport file and carried out an on-demand BPA. Some of the findings / recommendations are already done within our box. For eg: it says to ensure the Palo Malicious address list (EDL) should be included in outgoing and incoming rules as Deny. t...
Hello,I have an important question regarding User-ID Self-Signed Certificate expires on 18 NOV 2024 https://live.paloaltonetworks.com/t5/customer-advisories/update-to-additional-pan-os-certificate-expirations-and-new/ta-p/572158 What I understood this regarding User-ID if I have LDAP or DC for authentication but in my Palo Alto I'm using on...
reconnaissance protection alert search We have alerts set up but I need to search for the alerts but what is the search string
Hello all, I am thinking of how can i clean/organize my firewall policies. Many rules seem to be mixed up within each other. Do you have any suggestions to make it more appealing to the eye? How should I organize my rules?
Hi, I have a question about PAN-240612. ===== Fixed a kernel panic caused by a third-party issue ===== What feature does this issue relate to? And what exactly is “third-party”? BR
Hello For example, some implementations require multicast traffic to be encapsulated before IPSec encrypts it. If this is a requirement for your environment and the GRE tunnel and IPSec tunnel share the same IP address, Add GRE Encapsulation when you set up the IPSec tunnel.https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/networking/gr...
Good Afternoon, How do you apply for the academies listed in the early careers section of the main website?
the basic topology is: Internet FW are non-palo alto in HA A/P directly connected (no switch in between) to a pair of Palo Alto in A/A HA -in Vwire mode (no Layer 3 on the Palo Alto but in transparent-zone) then Palo Altos in A/A HA are connected to the Core switch where the rest of the environment connects to as well. The internet FW will send ...
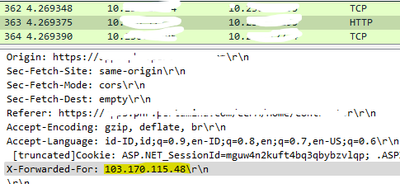
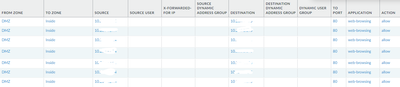
Hello everyone, I have enable x-forwarded-for in PA. When I look at the pcap from PA, I see the ip address but from monitor log traffic, collum x-forwarded-for ip is empty Please your help. Thank you
| Subject | Likes |
|---|---|
| 2 Likes | |
| 2 Likes | |
| 2 Likes | |
| 1 Like | |
| 1 Like |