General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! UNABLE TO PING MANAGEMENT INTERFACE FROM LAN

I have a fairly simple network setup in my LAB Management Interface 192.168.1.1 /24 LAN Interface 192.168.100.1/24 DESKTOP IP 192.168.100.100 I have allowed all the Internal Subnet on the Management interface which is 192.168.100.0 /24 in permitted list I cannot ping the Management Interface 192.168.1.1 FROM 192.168.100.100 NO SECURITY POLICIES ...
Resolved! Failover IPSEC tunnels with tunnel monitor keeps both tunnels active

We have just configured 2 IPSEC tunnels with a remote palo. Both sides have 2 IPSEC tunnels with tunnel monitor and DPD configured. For some odd reason, the when the primary tunnel is active and has active routes going to it, the secondary tunnel still shows active. Traffic is still flowing the way it should, I never see the traffic change to...

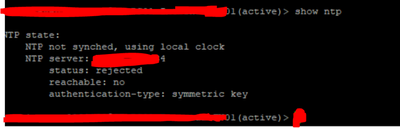
Resolved! NTP not working once authentication is enabled

Hi Guys, NTP was working well. But when authentication was enabled below msg is seen on the Firewall (NTP Stopped working) NTP server is a local one using IP address (not FQDN) PAN-OS Version 10.1.5-h1 All the other devices are syncing except for the Firewall. Has anyone else seen this issue? Any help would be greatly appreciated. Regards,...

paragkarki143_1-1663308368803.png
Pras by • L4 Transporter
  • 14124 Views
  • 10 replies
  • 0 Likes

Resolved! TYPICAL NAT QUESTIONS

Hello,I have a web server in DMZ with private ip address 192.168.10.100/24 and I would like all the traffic from outside should come to this server. My public ip is 1.1.1.2/255.255.255.248 which will bind to 192.168.10.100To perfom this I can create a destination rule FROM TO Source Destination Destination Translation Address (Static)Untrust--&g...

Resolved! GlobalProtect expand IP Pool

We have an existing GP setup and it's working, but the IP Pool is set to a range of IPs 192.168.10.10-192.168.10.100 instead of a subnet 192.168.10.0/24. I want to either expand the range or change it to a subnet. I tested this by expanding the range to 192.168.10.5-192.168.10.150, but clients that got an address in the newly expanded range ...

SAML Immediately logs me off???

Hello -I've set up SAML and by all accounts it looks like everything is working fine. In the Monitor > System logs I see four different events: saml-client-redirect, saml-idp-activity, saml-signature-validated and finally auth-success. The issue is this:I click on "Use Single Sign-On" > (same result with/without optional Username) Continu...

Shawverr by • L3 Networker
  • 5091 Views
  • 4 replies
  • 0 Likes

Updates required for NGFW customers of User-ID

Hi Team, Can someone please confirm if the incoming expiration of the certificate used by NGFW, and user-ID, going to impact Cloud Native solutions as PrismaCloud and Twistlock defenders? I'm not sure if anything needs to be performed before the date on some PrismaCloud defender which are currently monitoring the AWS Accounts. Version: d...

A_Canu by • L0 Member
  • 1366 Views
  • 1 replies
  • 0 Likes

tacacs+ authentication

Hi All, i need to undersatnd if tacacs+ is cisco properiety , so how come juniper and paloalto use it ? second question here , tacacs+ used mainly for cisco command authorization , so what is the need for that inside paloalto ?

Resolved! User-ID agent upgrade path

Greetings, I am running NGFW x 35 (10.2.10-h3) and User-ID Agent 10.2.2-111, which I believe needs to be upgraded to avoid the Nov-18 issue. My question is, does the User-ID Agent need to remain in the same stream as NGFW (ie. 10.2.x) or can it go to the 11.0 stream? A side question (because I inherited this environment) ...If I have the 'st...

Global Protect HIP Does Detect Firewall with New Apple MacOS Sequoia

Can you please provide some advise on this: Our client has an issue with the new Apple MACOS Sequoia The new Apple MacOS Sequoia seems to have changed some behaviour in how they check the local firewall. Currently Global Protect HIP does not detect if the local firewall is enabled. I have attached the information above. Apple Firewall:...

image.png
image.png
image.png
Salathiwe by • L3 Networker
  • 11181 Views
  • 9 replies
  • 3 Likes

Resolved! Upload Panorama License Key via API

Hi, I'm running Panorama in an air-gapped environment. As it stands, I have to download the license key from the Palo Alto Support Portal and then manually upload the key to Panorama. Is there a way this can be automated? Does the API support this method? I can't find anything that suggests that it does. Kind regards, Carl

C.Stuart by • L1 Bithead
  • 1843 Views
  • 2 replies
  • 0 Likes

Help me understand wildfire please!!!

I am having some trouble understanding the different wildfire options. Hoping someone can lead me to being able to understand. First of all - the wildfire profile itself:We have two sections - rules, and Inline Cloud analysis. What is the difference between these two sections? According to documentation: "The Advanced WildFire cloud operates a s...

VK9H13 by • L2 Linker
  • 3944 Views
  • 2 replies
  • 1 Likes

Resolved! postRequest() error: 'Error: device proxy - cannot connect to web server'

We have had problems with the graphic interface of some 3250 units. The units respond to ping and allow CLI connectivity, however, when I try to load the graphic interface from a browser it indicates that it is not possible to load due to connectivity problems, which is not true since the unit does respond to ping and CLI. We tried connecting di...

aalfaro by • L2 Linker
  • 4080 Views
  • 3 replies
  • 0 Likes
  • 24470 Posts
  • 125 Subscriptions
Top Liked Authors
Labels




