General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Incomplete release notes

Hello, why do I have to go there: PAN-OS 10.2.7-h6 Addressed Issues (paloaltonetworks.com) to find some unresolved issues in 10.2.8 ? i.e PAN-242627 or PAN-246431

How and Why to Accept a Solution to Your Post

Did you know that you can help your fellow community members by accepting solutions when a reply answers your question. Accepted solutions are a super-helpful resource in the community, and we want to make sure our members understand how this feature works! Why do accepted solutions matter? By marking a reply as an Accepted Solution, you cont...

JayGolf_0-1691518400714.jpeg
JayGolf by • Community Team Member
  • 12263 Views
  • 3 replies
  • 15 Likes

Basic Palo Alto configuration Help

I am very new to PA firewalls. To understand the firewalls I have setup a lab and also worked on the physical firewall. Following my topology PA - Switch - PA VLAN 100 Ip : 192.168.1.5/30 and 192.168.1.6/30 Zone WAN Mgmt profile : ping enable interface : L3 sub interface 1/1.100 - tag 100 Nothing else is configured. I am try...

gondolf by • L1 Bithead
  • 2862 Views
  • 2 replies
  • 0 Likes

Citrix Receiver on Globalprotect

I seem to have Globalprotect working fine for access to any internal resource.The one thing that does not seem to be working is the connection Citrix Receiver (PNAgent legacy version 13.3) makes to our internal Citrix Web Interface / Services site.I'm getting the error "citrix receiver could not contact the server. please check your network conn...

dieter_b by • L4 Transporter
  • 14948 Views
  • 5 replies
  • 1 Likes

Resolved! VM monitoring sources attributes/annotations

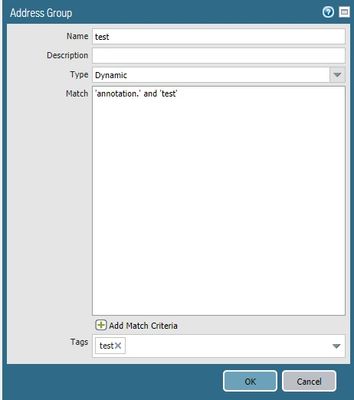
Does anyone know more on the use of the "annotation" field for use in a dynamic address group from a vm information source?Can the notes or tags field in the summary tab in vCenter be used to apply custom annotations? Any assistance on the syntax would be great since PAN dosn't seem to provide much on this that I could find.The goal is to be abl...

vc.jpg
dag.jpg

GlobalProtect and using split tunneling

Global protect has the handy feature of excluding select destinations from being sent over the vpn. For example, setting(Split Tunnel - Domain and Application - Exclude Client Application Process Name) https://docs.paloaltonetworks.com/globalprotect/4-1/globalprotect-app-new-features/new-features-released-in-gp-agent-4_1/split-tunnel-for-public-...

Resolved! USER ID MAX USERS IN A GROUP???

Hello,I've configured on PA5060 an Idenfication with AD:PA5060: 4.1.6 USER ID AGENT : 4.1.4-3LDAP SERVER 389 I do a group mapping by group but this group have more than 16000 users.when I do a show user usersIDS , I can't see all my users. I know that AD have a limitation of page size to 1000 users by request.do you know if they are an limit...

alle by • L3 Networker
  • 20513 Views
  • 10 replies
  • 0 Likes

Can't install device certificate

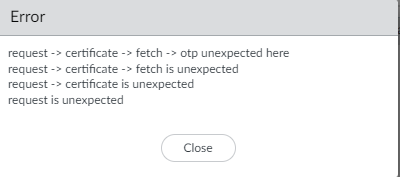
Hello, I'm trying to install a device certificate as instructed in the manual. I generate OTP using my account, I indeed see my valid serial number, get the OTP. Then I copy-paste to the firewall GUI and get the following error: I'm connected to the internet, did setup of DNS and NTP servers. Thank you very much.  

Screenshot 2024-04-17 173742.png
YonatanG by • L1 Bithead
  • 1935 Views
  • 2 replies
  • 0 Likes

TS agent SSL error

Hello, I've been trying to add a new TS agent on my firewalls. As there is no redistribution for user-{ip+port} mapping, I want to map the TS agent to 2 FWs. Backend FW is connected correctly, Frontend FW is in error.I can capture the following between FW and TS agent :- FW to TS : SYN- TS to FW : SYN/ACK - FW to TS : ACK- FW to TS : RST I've g...

MMerlier by • L1 Bithead
  • 7615 Views
  • 4 replies
  • 0 Likes

Resolved! Edit personal information

I'm trying to update some personal information (my last name), but when i save the configuration, it doesn't actually save. On the other hand, my last name changed and now its my name (Lucas Lucas). Please help me, i can't find any Customer Service number about problems like this one, only TAC.

loropeza by • L1 Bithead
  • 2072 Views
  • 2 replies
  • 0 Likes

403 forbidden error while importing IDP fiile

Hii, I have been trying to import G suit IDP file in SAML Identity provider on palo alto VM firewall but for infinite time its just showing message "uploading" without showing any error message. when I checked in network tab of inspect element I can see the error 403 Forbidden. Not sure why its coming like this as same IDP file I am able to ...

Resolved! PING from Firewall GUI

Hi All, I have a basic doubt.Isit possible to ping from firewall GUI ?If not from Panaroma CLI, isit possible to connect firwall ( to test the ping from firewall to host ) Reason : To check the network latency from fireawall. ThanksKM

  • 24479 Posts
  • 125 Subscriptions
Top Solution Authors
Labels