General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! vulnerabilities detected on https://appvpn.xxxx.xxx through our Bitsight

Hi team, We use a cybersecurity tool called Bitsight in order to discover vulnerabilities in our organization. This time the tool has found out some in our https://appvpn.xxxx.xxx subdomain which is a web portal to download the GlobalProtect client. The Bitsight finding in this case are related to the Content-Security-Policy header config...

Alpalo_0-1718719318523.jpeg
Alpalo by • L4 Transporter
  • 5068 Views
  • 2 replies
  • 0 Likes

DHCP Server - Conflict IP's

Has anybody else experienced an issue with their DHCP server leases being constantly filled up with conflict IP's by one device? There is no pattern to which device will do this, it seems at random. I'm on version 11.1.6 Any guidance would be much apricated.

CPATT_0-1771337718677.png
CPATT by • L1 Bithead
  • 966 Views
  • 1 replies
  • 0 Likes

Assistance with LDAP Authentication

Currently working on a PA-540 running 12.1.3 code. I have setup a LDAP server profile, and setup an authentication profile. If I test from the cli, the bind is successful, but the authentication fails, even if I use the same credentials I used to do the bind. I've also tried this with a domain admin account in case it was a permissions issue ...

DJ_1924 by • L2 Linker
  • 1124 Views
  • 2 replies
  • 0 Likes

Move FW to a TEMPLATE VSYS

Hi, I have created a new vsys in a 5220 to have all the config that we have in a VM FW. Which is the best way to move all the FW VM config inside the new VSYS in 5220. Copy all the FW VM config and paste it in the template VSYS in panorama? Is there an way to do it by GUI?

BigPalo by • L4 Transporter
  • 512 Views
  • 1 replies
  • 0 Likes

Resolved! Management IP in Active/passive setup

Hi I am quite new to Palo Alto firewalls, but have worked with different vendors before. When running a HA in Active/passive a central VIP for mgmt is usually setup, so you dont connect to the passive FW.From what i see there is no VIP for mgmt in the HA setup i am working on here. Is that something that is setup wrong or ? We have a dns name ...

HA ACTIVE firewall is failing when commit

The problem is that after performing a Commit&Push, the primary (active) firewall generates a status change that affects the signaling of the Cisco Nexus switch ports, causing them to enter suspended mode on both switches in the VPC configuration. After the switch stops seeing the primary firewall, the primary firewall does not switch. Disco...

F.Pinar by • L3 Networker
  • 899 Views
  • 2 replies
  • 0 Likes

Resolved! About threatID action.

The followin theatID action is "Alert".Would you tell me the reason why action is default set to "Alert"?Would you tell me if there is policy for the default action? 30941316843197132351343213475736415391543990954465548015905585253866469016693719 Best Regards,Atsushi Takara

Configure VPN GP wit Microsoft Authenticator

Hi, i would like to configure my VPN using MAuthenticator. Anyone has a guide for this? i was checking this link but im not sure if this config should be used if you have EntraID AD in the cloud or not: https://learn.microsoft.com/en-us/entra/identity/saas-apps/palo-alto-networks-globalprotect-tutorial We have AD in server onpremise.

BigPalo by • L4 Transporter
  • 3301 Views
  • 3 replies
  • 0 Likes

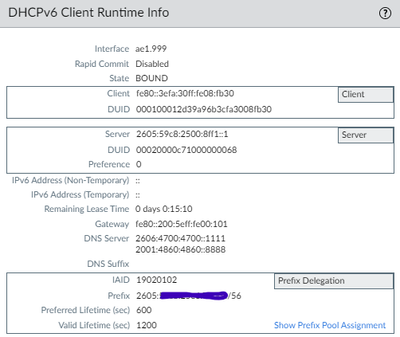
PAN OS 11 and DHCPv6 with Prefix Delegation

I wanted to make sure I had the settings correct for configuring DHCPv6 on my WAN interface for Starlink. I can confirm that I did get an allocation of IPv6 addressing with a /56 prefix and was successfully able to get an IPv6 address assigned to my internal interface. The issue is, it appears I have not gotten an actual perm or temp address o...

ChazKlinkbeil_0-1705503939918.png

Resolved! Blocking Google Games

Has anyone had any success in blocking the Google browser based games yet? I have seen a few threads with no answers. I'm going to bust out the Fiddler and see where it is going during this but I don't want to interfere with normal users and their Google searches. I was thinking there would be an app-id for it but I may have to find domain nam...

Resolved! PAN-OS-PHP Combining actionss

Hi I am trying to use the PAN-OS-PHP to bulk edit some rules. My question is can I chain/combine actions together. The documentation says that I can but when I try I get a syntax error Before I send the command to the Firewall I just want to check the rules that will be updated I don't think I am to far away but its just the sytax. If a...

PAN-OS-PHP-Action.jpg

PAN-OS 12.1, IPv6 and Region/GeoIP

Hi, With PAN-OS 12.1, IPv6 addresses are now also showing what Region they belong to. However, this seems to be limited to logs. Security policies, using specific regions/countries, will still not match the IPv6 addresses, even though the same IPv6 addresses shows the appropriate country code in the logs. Is this a known issue (internally perh...

TCP-RST-FROM-CLIENT and TCS-RST-FROM-SERVER

Hi All, As captioned in subject, would like to get some clarity on the tcp-rst-from-client and tcp-rst-from-server session end reasons on monitor traffic. Even with successful communication between User's source IP and Dst IP, we are seeing tcp-rst-from-client , which is raising some queries for me personally. Are both these reasons are normal ...

Jimmy20 by • L2 Linker
  • 326831 Views
  • 7 replies
  • 2 Likes

Expired license CDSS

Hello, we received an alert regarding the expiration of CDSS licenses on February 11, 2026, following a change in operation on the Palo Alto side. All our equipment is running at least version 10.2.13-h5. The partner portal does not show any affected devices. We would still like to know if this will have any impact on certificate management, act...

  • 24454 Posts
  • 125 Subscriptions
Top Solution Authors
Labels