Resolved! Panorama version vs firewall version
HI , We are planning for 10.1.6-h6 firewall upgrade .Just wanted to confirm for Panorama we need to have minimum 10.1.6 version ? @PavelK
A group within my company would like access to, we will just call it, xyz.com/blog, but we currently block xyz.com via an EDL based policy. We are also not decrypting this groups traffic as it causes issues with some of their connectivity, so options are limited in that respect. I added xyz.com/blog to our whitelist just to see if it would work,...
When I tried resolve the FQDN, abc.com, and it shows 4 IP address of 54.192.150.W, 54.192.150.X, 54.192.150.Y, 54.192.150.Z use this address ipv6 not resolved. After I performed 'request system fqdn refresh force yes’ The resolve FQDN shows another 4 IP address of 13.33.33.W 13.33.33.X use this address 13.33...
hello, anyone ever have this following issue. on some of our template stacks the shared template values are not passing through to the template stack. in the template stack some values come through from the device template but the shared template (which is delow in order the device template stack) values do not come through but only on some fiel...
Hello - Can someone explain the difference between "vsys1 - User-ID Hub" and another of my palo's that just has "vsys1"?
Morning all. We are onboarding 90 or so pa410 firewalls and did our initial config and update with ZTP, at which point panorama showed the managed devices as their DHCP address on a /24 I gave them. we are now using the dedicated WAN interface for services and mgmt, these remove branches only have a single handoff. In device summary the device...
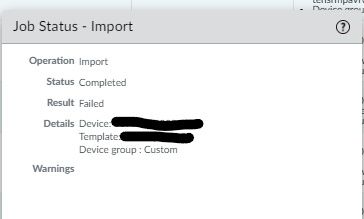
Hi, I get following error, when importing config of new firewalls i am trying to onboard into Panorama.
Just looking of for clarification around google-docs app IDs. If I allow the google-docs container ID in a policy\app group...I'm essentially including ALL the child apps contained within.... correct. ??? No need to explicitly specify the child apps ??? ie.... google-docs-base google-docs-uploading google-docs-editing etc etc Appreciat...
I am working with a customer whereby the requirements are to split different traffic by different interfaces. Its an internal firewall and will not route internet traffic 1x Interface for East/West/North/South traffic 1x Interface for communications to Panorama 1x Interface for any communication to internet targets the firewall needs(NTP/Licen...
So I purchased premium support for my device but when I go to the website to create a support ticket, I get to a point where the ticket is blocked by a window telling me that I am being redirected to the live community. If I click continue a new tab opens to to this site. If I click cancel they close my ticket. There is no way to go back to the ...
Is there a way to configure the boxes to act as a NAS by sending a Radius Server (like Freeradius) accounting information? I am particularly interested on the session start and session stop attributes. I am about to provide Globalprotect VPN access to a community of users and need to account the resource use in the same Radius server where the a...
Hi All,We are running PA with firmware 9.0.4 Getting errors while "disabling" not required/unsed IPSec tunnel. Error: tunnel interface tunnel.50 encap interface is not set.Error: parse tunnel member failed.Error: error parse qos tunnel groupError: error parse tunnel-traffic group listError: alloc obj iterator failedError: QoS configuration error...
Hello All, from the GUI i can get all the security policies from one zone to another, However, from the CLI, is there a way? for example : i need all the policies from Orange_Zone to Free- App_Zone "Orange to DEVDB11-1; index: 1333" {from Orange_Zone;source 172.24.x.x/24;source-region none;to Free-App_Zone;destination 172.24.x.x;destinatio...
Hello! I have a Palo Alto with version 9.1.5 installed and I want to install a User-ID Agent, which version can I install?
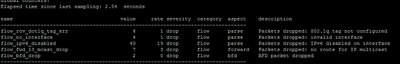
Hi All, Is there any way to check which source of this flow_ipv6_disabled? Our monitoring tool keeps on alerting us due to these parse packet drops. When I run the command below, I don't see any logs on Palo Alto's monitor. debug dataplane packet-diag set log counter flow_ipv6_disabled Thank you in advance.
| Subject | Likes |
|---|---|
| 5 Likes | |
| 3 Likes | |
| 3 Likes | |
| 1 Like | |
| 1 Like |
| User | Likes Count |
|---|---|
| 5 | |
| 4 | |
| 3 | |
| 2 | |
| 2 |






