General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! User-ID-Agent wrong mapping with specific IPs

Hello,since a few days we see strange things with User-ID-agent.For some specific IP-addresses there are shown wrong users. This users even are not in the internal AD, they are just external VPN users invited from Azure. But they are mapped to internal ip addresses. Even if they are not online over VPN.When looking into Monitor - User-ID in the ...
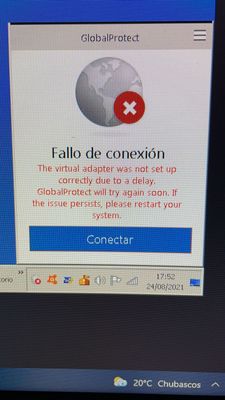
Global Protect error Windows 7 Client

Good afternoon, first of all thank you very much for the help and support for this case: "The virtual adapter was not set up correctly due to a delay. GlobalProtect will try again soon. If the issue persists, please restart your system" -Windows versión: Windows 7 64bit SP1-Global Protect Client: 5.1.8 64bit I have already restarted the computer...

Error_Gprotect_Win7_2021-08-24 at 17.52.48.jpeg
Metgatz by • L4 Transporter
  • 3496 Views
  • 2 replies
  • 0 Likes

Resolved! VPN to AWS with BGP

Hello, I have 3 locations that I need to create VPNs to AWS for. Each location is dual ISP using PBF. Since AWS uses 2 tunnels each VPN connection, seems there will be 4 total tunnels per location (2 per ISP). My initial thought was to use static routing but I'd like to avoid any asymmetric routing from AWS. In these locations, we are usi...

mnashe by • L1 Bithead
  • 13107 Views
  • 5 replies
  • 0 Likes

bgp cmd

Hi All , Just checking what cmd we can use to validate receive and adversities BGP route from a peer like we have in cisco . @PavelK

Resolved! Security Policy - US access only

Hello, I'm trying to configure a Security Policy to only allow US-region IP addresses to hit our network. I added as a first rule to allow any untrust us region to destination untrust US region. I am not sure if this is correct. maybe I'm allowing all traffic within US, that probably is not supposed to be allowed. thanks #urlfiltering #r...

YParreno by • L1 Bithead
  • 4712 Views
  • 3 replies
  • 0 Likes

Resolved! Firewall is not forwarding logs to Panorama

Hi Folks, We have PA-3250 firewall deployed in our environment managed by Panorama. The panorama is deployed in Panorama mode and the firewall is under panorama and no connectivity issue between firewall and Panorama. The firewall is also added under log collector group setting in Panorama. Configuration vise everything is good. The fire...

Can we continue to check domain and antivirus if GP license expired

In Global Protect HIP check we have allowed only specific domain machine and specific antivirus. Firewall will continue to check domain and antivirus if Global Protect license is expired ? Any impact if GP license expired ? Do we require to remove HIP profile from rules in such case ?

Deepak25 by • L3 Networker
  • 2485 Views
  • 2 replies
  • 0 Likes

Resolved! unkown-tcp/udp session timeout?

Dear all,What is the session timeout for unknown-tcp/udp?Since this is an application which has no values set for timeout, can I conclude it will use the default-tcp/udp timeouts?Kind regards

mr.linus by • L4 Transporter
  • 8673 Views
  • 5 replies
  • 0 Likes

OpenVPN support on Palo gateways?

Palo gateways have supported ipsec site to site vpn for a long time. Do they also support acting as an OpenVPN gateway? I dont mean openvpn passthrough to a backend. I mean actually being the Openvpn endpoint.

Resolved! Found a PA 200 in the trash

Hi, i found a PA 200 in the trash, it works fine, is it viable to use it as a firewall. I don't have access to any support at all. Not even a os update of some kind. And is there any way i can get said update. Have a great day.

RobFut by • L0 Member
  • 2208 Views
  • 1 replies
  • 0 Likes

revert but not the config

Is there a way to "revert" via cli? I don't mean config changes either, I mean like the following places: 1. Network > Interfaces > Ethernet1/1 2. Device > Setup > Management I'd like to script out reverting these.

RobertShawver_0-1658516753160.png
RobertShawver_1-1658516827275.png

Resolved! Port Shutdown

I don't think there is, but just double checking. Is there anyway via GUI or CLI to shutdown a port on the Palo? There are times when I would like to do some configuration, such as sub-interfaces and so on to an aggregate group that is plugged into the core switches. At times this can cause an issue so I would like to be able to shut the por...

We cannot export the metadata, when you are in the FW, in the Global protect section, it does not allow you to enter the IP or the Vsys.

Hello, We cannot export the metadata, when you are in the FW, in the Global protect section, it does not allow you to enter the IP or the Vsys. When I select in the Authentication Profile, the profile from which I want to export the data, and I select the Globalprotect Service, it does not automatically show the VSYS,and select the Globalprote...

Alpalo_0-1658385538610.png
Alpalo_1-1658385590433.png
Alpalo by • L4 Transporter
  • 2961 Views
  • 4 replies
  • 0 Likes

Access denied

Hello Palo Alto Community , I have problem in communcating betwen Fire wall and Domain Controller (ldap).Status show me Acces Denied on Server Monitoring,i try change user roles to fix it , but again show me the same status Acces Denied . Please help me !

Global Protect on IOS Always ON VPN sanity check

I've had a Palo Alto case open for almost 9 months now that appears to have devolved into a finger pointing match between Apple and PAN and I'm going to have to make some decisions here, I don't know if anyone else uses that functionality or not. Apple re-wrote the VPN APIs around IOS version 12.1 where they only allow "Connect on demand" (AKA ...

  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





