General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

System log message Clearing snmpd.log due to log overflow

I am wondering why I see the log 'Clearing snmpd.log due to log overflow' on several of my firewalls. Out of the ~20 firewalls I manage 2 or 3 firewalls log this message on occasion. The other firewalls never log this message. I am trying to understand why this occurs on just a few firewalls. Should I be concerned about the message? What do I lo...
SNMP and Netflow

PAN 9.1.8 has SNMP V3 configured base onhttps://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClHOCA0with Netflow on AE5.30, ae5.50, and ae5.60 of the 5260 base on https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/monitoring/netflow-monitoring/configure-netflow-exports.html#id4ad7a523-e577-41ab-8b77-4034458a2a7b On m...

arhong by • L1 Bithead
  • 4753 Views
  • 5 replies
  • 0 Likes

Content filtering for MAC OSx

I am trying to finalize my content filtering for our PA 820 rollout. I have the user-ID, group mapping and content filtering rules (By group) working just fine for my windows PC's. Where I am stuck is trying to figure it out for all of our MAC OSx users. None of our MAC's are joined to our domain and I am not sure about adding them at this time....

RussMc by • L1 Bithead
  • 3225 Views
  • 2 replies
  • 0 Likes

Resolved! PA Packet Capture Data Storage Location (CLI)

I’m trying to figure out how to view the data location of an in progress packet capture in the CLI. I’m aware of the current packet size in the GUI, but I would like to see where the data is logged in the CLI along with the current available storage remaining.

IsaiahF by • L1 Bithead
  • 4482 Views
  • 2 replies
  • 0 Likes

OSPF stopped gracefully restarted

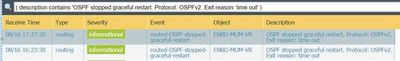
Hi Team, We are facing issue with OSPF is not working properly over the firewall as per the configuration part seems fine we checked with the below given document.https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000Cm5ZCAS All the configuration for HA is configured as per above given document.We checked with the configurati...

OSPF issue.jpg

Log redistribution after adding additional log disk.

Recently we added a 2TB log disk to this virtual Panorama running 8.1.19 on VMWare ESXi 6.5 Once adding, the log redistribution process on the local log collector started as has been progressing very slowly. Over the course of 15 hours this job progressed to 7% >show log-collector all...... Redistribution status: pending --- 7% How long...

can we forward logs to two different logs collectors from same fiirewall?

We want to store log copy on two collectors for redundancy.Note : We don't want to go with collector group(with both collectors in same group) config with redundancy, as this config half the space.Example. Panorama M200 is in HA with above config , we get search engine quota in single panorama is 7.5 TB.Search Engine Quota Stats: Total Disk(s) S...

Deepak25 by • L3 Networker
  • 2644 Views
  • 2 replies
  • 0 Likes

User is trying to connect with MS-RDP. Log shows TCP 3389 but application is not-applicable

We've got a remote user connecting with GlobalProtect. He's trying to RDP to a PC on our inside network. There is a security policy that he should be matching- traffic matches source and destination zones, user-ID is matching the right group, HIP check is good. it seems to be failing to match the policy because it's not matching on the appl...

Resolved! Global Protect MFA Vendor Support

I am a bit confused with the MFA vendor supported by the firewall, because the Compatibility Matrix says that MFA server profile is not supported for Global Protect?https://docs.paloaltonetworks.com/compatibility-matrix/mfa-vendor-support/mfa-vendor-support-table.html# I am aware that any MFA vendor can be configure over Radius Server, but pre...

BatD by • L4 Transporter
  • 10891 Views
  • 6 replies
  • 0 Likes

Is there CLI - Enable and Commit Policy

Dear all, Since my WebUI is not responding even with a system reboot and management restart by CLI, SSH works fine, Is there a way by CLI to enable and commit Policy? Any help would be greatful. Thanks, Sean

Resolved! RADIUS And Open LDAP Integration.

Hi team, I have come through as a requirement from one of my clients, They are using RADIUS Server for RSA authentication for globalprotect, but in USER ID they are using OpenLDAP, So in the ip-user-mapping, Whenever user connecting to globalprotect, I can see the user detecting from the GP and the only as "username", but the customer has config...

PA blocking windows updates?

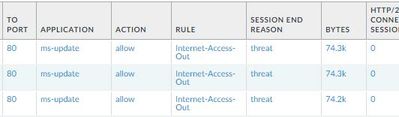
Howdy, Trying to figure this out. It almost seems that our pa220 is blocking windows updates. See my first pic, does session end reason threat mean it stopped the connection? I ask because I cannot get this update to download on any windows 10 pc in my environment see pic 2, it starts to download and stops at 2% then errors out. . Yet it will do...

fw1.JPG
fw2.JPG

Resolved! IPSec tunnel creation issue

Hello all, one of our customer is trying to create the IPSec tunnel between PA and Fortigate. When phase 1 is initiating in main mode negotiation failed error and we find error in system logs: 2020-02-18 14:55:18.010 +0200 [PERR]: { 12: }: Expecting IP address type in main mode, but FQDN.2020-02-18 14:55:18.010 +0200 [PERR]: { 12: }: 197.157.129...

Logesh by • L1 Bithead
  • 17819 Views
  • 9 replies
  • 0 Likes

Resolved! High Availability for Firewalls in diferent locations over Layer 3 network

Is it possible to configure high availability between Palo Alto VM series Firewalls that are located in different buildings over a network to connect both firewalls? I have two VM-300 Firewalls that are Active/Pasive with Global Protect in the same physical Server, which will result in a single point of failure. Recently there was an electrical ...

  • 24454 Posts
  • 125 Subscriptions
Top Solution Authors
Labels