Resolved! How to filter policies by zone
Hi, Is there anyway to filter the policies by zone? or other parameters? Is there any guide about this? Thanks a lot.
I've been doing mixes of internal and external gateways with customer forever (I usually forget that "always-on" must be enabled for internal gateway detection to even be allowed in the first place). I'm working on a pre-logon implementation that also would benefit from leveraging internal gateways/no-tunnel while inside the enterprise network...
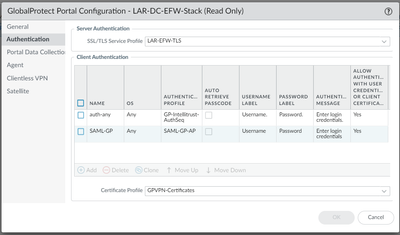
Greetings all, I hope you can help me. I currently have Globalprotect set up on a single firewall - both portal and gateway. We're using Radius for authentication, it is working well. We want to transition to SAML. For testing purposes, we'd like to have SAML configured for a specific test user (or group), while leaving the current authentic...
Problem: Because of occasional issues with vendor patches, like MS had early this year, (see URL below), very few companies release patches/updates to clients or servers on the day of release. They test the updates first, then release them days or even weeks later after testing has shown no major issues. GlobalProtect has no capability to delay ...
Hi, a site I am working on with a client is being flagged as Grayware. This is a landing page for a digital agency product and shouldn't be flagged. Can this be reclassified? This is the domain: https://audiencexlerator.com/ Thanks in advance, Matt
tl;dr use the command "cu" instead of "screen". I have been trying to factory reset a PA-3200 for about 45 minutes. I am using a standard RJ-45 to DB9 serial cable with a USB serial adapter. Following the instructions I get to the step where I have to select the factory reset and it says "maintenance reason". Hitting "q" to go back a screen...
Hello everybody, How many policy we need for block and review source of infected hosts? One or two? Internal dns is using but we can not see source of users.
All our 10 devices throws there errors (medium severity) since Thursday. TAC has no response for this. Anyone?
Hi all, A colleague of mine asked if it was possible to search for specific URLs or IP addresses in PAN hosted EDLs, to help figure out which EDLs they might be part of, which i found out it's not. It's pretty tedious to go through all the EDLs at https://docs.paloaltonetworks.com/resources/edl-hosting-service, so i decided to add this feature...
We selected the paid PA-VM subscription that includes the 15 day free trial. It looks like it won't be fully licensed until the end of the 15 day trial period. Can we skip that and enable now to get access to the support portal and wildfire api key?
Hello Folks, I am looking for a ways to detect the attempt for this vulnerability through SIEM. Based on the blogs available the vulnerability can be exploited by accessing URL with "unauth" on management interface. So I am thinking to look for web interface access logs with keyword "unauth". However, I would like your help to get below detail...
Has anyone ever done tunnel-over-tunnel on the PaloAlto (to Cisco/etc.)? I have been having problems getting traffic to return to a remote site. I normally have multiple IPSec tunnels to remote sites (carrying specific isolated VLAN/networks) over a private WLAN, the tunnels tied to specific Network Zones on the PaloAlto. Recently I had to setup...
On our PA-1410 under Network - GlobalProtect - Portals - each of our portals (one on each interface for each ISP) - Agent - Agent Config - External Gateway I added gp2.domain.com to go along with gp.domain.com. I was thinking (hoping) that would update the GlobalProtect client to add the gp2.domain.com to the GlobalProtect client as a failover ...
We have upgraded our FW to 11.1.4-h7. After the upgrade the IPSEC tunnels were working fine. But from the past 2 days we are observing that tunnels are flapping and one of the tunnel is down due to phase-1 negotiation failure due to timeout. Does anyone else facing the same issue? or faced the issue earlier like this?
Hello everyone, maybe this is a silly question, but as far as I can see the current PAN-OS 10.2 preferred release dates back in november and does not include fixes for recently discovered vulnerabilities (CVE-2025-0108, for example). I usually put a vulnerability protection profile in front of my management networks, but this vulnerability i...