General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Custom reports problem

We have problems with creating custom reportsWe configured custom reports as we need pointing the time interval for one month but the report shows us only two last days of the previous month.i can also show you admin@PA-3020> show system logdb-quotaQuotas: system: 4.00%, 3.231 GB Expiration-period: 0 days config: 4....
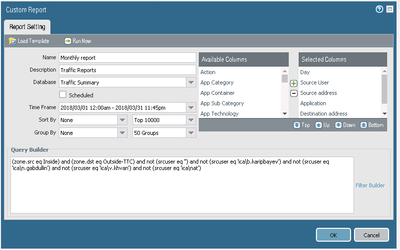
image001.png
Radmin_85 by • L4 Transporter
  • 4898 Views
  • 5 replies
  • 0 Likes

Resolved! NAT LOGGING

Hello, I am a newbie so please bear with me, I Have a very simple LAB with a Palo Alto firewall with 11.00 Ver and an internet connection.I know that to provide internet connection to the user i would need a Policy,default route and a source NAT. Lets suppose I dont have a Source NAT for the internet connection, how would I know that I am ...

ECMP With PBF

Hi, I have ECMP with PBF configuration for dual ISP. ECMP using weight 100 on ISP A and 200 ISP B. PBF rule user A to isp A, user B to ISP B. default routing to ISP using the same metric we expect that user A will go to ISP A, but in reality user A is expected to ISP A, but we saw on the log several user sometimes is still go to ISP B, even ...

Why would what worked in Sophos would not work with PA

Hello everyone, Trying to make my ubiquity unifi access points with multiple ssid tagged with their own vlan IDs work with PA. it worked seamlessly with Sophos but can't make it work with PA. I have one Ethernet port L3 configured with subnet DHCP, DNS and assigned to office zone. Acces points are connected to it via smart switch which is ...

Resolved! Error: Threat database handler failed (Module: device)

I got two devices 3020 and is running with HA Active/Passive.First, I have download and install "Application version 384-1877 (07/18/13) and Threat version 384-1877 (07/18/13)" on the Active device and I select Syns ... to peer.After that, I issue "request restart system" on the passive device.Next, when the passive device reboot sussesfully, th...

same subnet multiple VRs not working

I am trying to setup SDWAN, however this firewall currently has several Site to Site VPNS which causes an error on deploying site to site vpns. I am trying to setup a second WAN address to be usedonly for SD WAN. Currently my public ip is 2.2.2.2/24 on ethernet1/2. I converted it to a trunk vlan 2 (2.2.2.0/24) as the native vlan and the tagged v...

mmercald by • L1 Bithead
  • 1742 Views
  • 1 replies
  • 0 Likes

How configure to receive email when an Importan action is required

Hello, From my colleague I have received the info about Upcoming November 18, 2024 Deadline for NGFW User-ID and Terminal Server (TS) Agent Certificate Expiration where I need to set and receive that Important Emails? is because I'm the responsible of all PA's Firewall on our organization but I don't know where subscribe to receive that ema...

S.Liloia by • L0 Member
  • 1041 Views
  • 1 replies
  • 0 Likes

Receiving too many alerts when a ISP or Tunnel link goes up or down.

Hello. I have a Palo Alto PA-440 We have enabled path monitoring for our ISPs, with the destination address/monitor IP set to 8.8.8.8. The ping interval is set to 3 seconds, and the ping count is 5. Additionally, we have configured and enabled system email alerts for the severity level "Critical". As soon as any of the ISPs is down or the route ...

System-log-test --1.png
Rehaman by • L0 Member
  • 1477 Views
  • 1 replies
  • 0 Likes

PA- Security Policy Destination as FQDN issue

Dear Community, I am facing an issue were the i have post security rule allowing the access to some FortiGuard URLs, on the other hand i am have a default deny rule with reset-both action right above to the interzone & intrazone policies. What actually happening is the traffic will hit the allow policy and right after will hit the default...

Unable to access HTTP & HTTPS

When I switch from passive to active, I can't access the application via http and https. But I can ping and telnet the application via port 443

thanhlb by • L1 Bithead
  • 2929 Views
  • 8 replies
  • 0 Likes

Split Tunnel - Exclude Client Application

Hello, I am setting up a new Global Protect gateway. We previously havent setup Global Protect (GP) before with Split tunnel so this is my first time and its not going smoothly..i am trying to exclude client applications for some software we use. being a media company, we often need to tranfer large files to partners. there are well known applic...

DevPatel by • L1 Bithead
  • 2226 Views
  • 3 replies
  • 0 Likes

videoparse.jar detected as Grayware

"videoparse.jar" is detected as Grayware in Wildfire but not found now. why this was flagged malicious ? File hash : 844ccde43fa61803f1643401600e17dced86c60509ee340ae83b332a068f8dcc VirusTotal - File - 844ccde43fa61803f1643401600e17dced86c60509ee340ae83b332a068f8dcc

  • 24483 Posts
  • 125 Subscriptions
Top Solution Authors
Labels





