Region Blocking
Hello everyone. I want traffic only from my own region. I want to block all other regions. How to do this process in a simple and short way?
We have support and other license like threat,WF etc cgoing to expire in 20 Nov 2019We got authorization code from the vendor with new date 20Noc 2020. Will Firewall will automatically renew the license and how? When I click on GUI retrieve license from license server nothing happens it still shows date of 2019
We have upgraded only Panorama to panos 10.5 , after that we are getting below system alert from all firewalls :SYSTEM ALERT : high : No valid device certificate found What is the meaning of this alert ?We haven't enabled the features mentioned in below link , still we are getting this alert for all managed devices https://docs.paloaltonetworks....
Hello,We have an object so that from the wifi networks for mobile devices (mobile or tablets) if you connect by a pc to it can not go out.We are doing this for the Vulnerability with the Threat id XXXX with the condition Pattern -mach http-req-headers and there are different headers.The problem is that when the traffic is HTTPS it does not show ...
Having an issue logging into an online marketing screen tool called screencloud. The browser throws a CORS error once they hit login and the web application throws Unexpected_API_Result. The only way for our marketing staff to sign into this specific service is to use their personal device or cell phone. Any company equipment either on site or...
I have been adding IP wildcard objects into security policy rules and they have been working until yesterday when I added some new rules with several wildcard objects. I have looked on the support site to see if there are any limitations on how many wildcard objects you can use in a rule and/or in a policy and I have not found anything. I have...
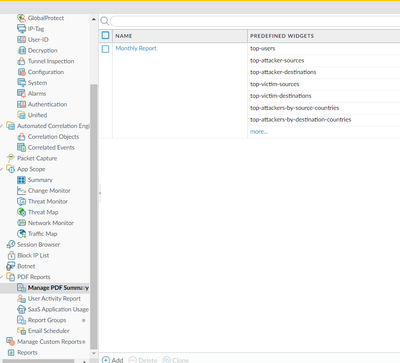
Hello, our user using PA850 and PAN 10.1.3 and they want to generate PDF Report for 30 Days.They was config the Managed Report PDF last week, and when they came to Reports, the report is empty.FYI, the device is deploy about 2-3 week ago, should i wait to 1 month for the report create automaticly?The reports can download PDF but only 1 day,but n...
Hello everyone, If I have the valid WF license and I enable the forwarding the RAR & JAR type. What the WF does when RAR & JAR file is being received? Does it analysis thoe files located in a JAR or RAR archive? Just wanna know.Thanks
Good Morning All, I'm relatively new to the PA world, we recently moved away from Meraki MX devices and have upgraded to a PA820 for our main office and PA220s for satellite offices. I have a couple of linux users that are having issues with not being able to use CLI tools and the menus are scaling strangely in 5.2.6.What do you folks see as the...
We are having a huge problem with only one of our syslog destinations. Instead of sending the syslogs as they are generated, the firewall is collecting them into a huge file (10-40GB) and sending this a few times a day. This is ridiculous and is making the syslogs useless. It is only doing this for one of 4 syslog servers. Percent utilization of...
Hi, We have added the PAN-DB private cloud server IP address in the firewall. but we were unable to get the license from M-600.we are getting TCP RST from Client error. could please advise me what is causing the issue Thanks in advance.
Hello. I have read only access to our firewall and in the past could do the command show config running and see all the rules in use. Now, I don't see near as many as used to. If I go to the web GUI and Monitor tab for instance, there is a rule named APP34-ROW-09-PAN that's actively allowing or denying traffic. If I search this in the cli ou...
Hello everyone,What I read the best practice is to enable log at session end, is there any use case to enable log at session start?any thoughts?thanks
Hello all,I am running PAN-OS 10.0.1 VM series firewall in VMware workstation. Currently I have a windows 10 VM machine behind the firewall. My interfaces are set to eth1/1 is the outside interface which is set to my home network. Eth1/2 is my inside interface which is set to a 172.x.x.x/24 subnet. I have a default route point to my home route t...
Hi,I have GP configured using LDAP for authenticating. Now i would like to configure LDAP with OTP (Google authenticator). So i have several questions:-Its possible to configure LDAP+Google authenticator? is there any procedure o manual to help?-In order to not impact in the current GP connection. Its mandatory to use another public IP for this ...