General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
cancel
Showing results for 
Show  only  | Search instead for 
Did you mean: 
Announcements
Scheduled Maintenance: November 14–15 (starting Nov. 14 at 12:00 AM PST)
LIVEcommunity will temporarily operate in read-only mode as we prepare to welcome Idira!
Public content will remain accessible, but log-ins, posting and community interactions will be paused during this period. Thank you for your patience!
General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.
About General Topics
Post a discussion here if you have general questions regarding configuration and troubleshooting for Palo Alto Networks products. Use this forum to collaborate with like-minded security professionals to improve your security posture.

Discussions

Resolved! 2 ISP Setup

Hi Team, I have a requirement to setup 2 ISPs terminating directly on firewall. 1 as Active and the other as Standby. We will be using Static routing with higher metric value for the Secondary ISP. If Primary goes down then Secondary should still allow access. But i have a concern if i can create 2 NAT rules with same source and destination as I...

Resolved! PA220 so slow rebooting

Hi, We have a PA200 which takes a long time to reboot. its like 13 minutes. Is that normal for PA220 ?? any way to know why its taking this time?

BigPalo by • L4 Transporter
  • 23458 Views
  • 9 replies
  • 2 Likes

Resolved! Howto delete sub-interace from cli

Hi,I`m trying to delete a sub-interface from CLI but cant seem to find the correct command, i managed to remove the IP address and tag but not the entire sub-interface.admin@PA-200# delete network interface ethernet ethernet1/4 layer3 units ethernet1/4.20 Server error : ethernet1/4.20 cannot be deleted because of references from:import -> net...

u18830 by • Not applicable
  • 26272 Views
  • 16 replies
  • 0 Likes

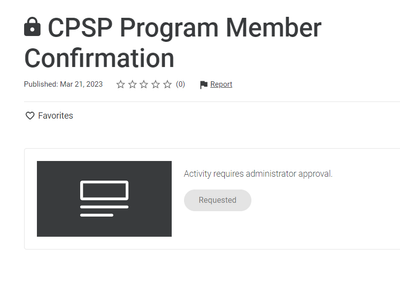
CPSP Program Member Confirmation

Hello, I am both domain administrator and super user in paloalto. And, we are partner. I need to get Micro-Credential for Cloud Security Consultant (PMCC). It needs "CPSP Program Member Confirmation". And, I send request and it says, "Activity requires administrator approval" -requested. I wonder who should approve this request. My adminis...

JahidAliyev_0-1710419244646.png

Threat Prevention - Qualys PCI

Hi all, I have a bit of a dilema here and hoping somebody may have some ideas.... We have threat prevention profiles applied to security policies relating to traffic entering our DMZ from the internet.We have PCI obligations and use Qualys' PCI scanning services.We are receiving a PCI fail during the scanning process due to the threat prevention...

GMHBA by • L1 Bithead
  • 13526 Views
  • 10 replies
  • 0 Likes

Resolved! Expand Log Storage Capacity on the Panorama Virtual Appliance

Hi everyone,I'm using Panorama 8.0.5 in Legacy mode on ESXi 6.0, I've 2 virtual disks: virtual disk 1: 52GB for system virtual disk 2: 500GB for logging storage.Now, I want to expand the size of logging storage up to 2TB. So can I just changing the size of current disk 2 from 500GB to 2TB or I have to add another 2TB virtual disk 3 the...

Hongson by • L2 Linker
  • 6363 Views
  • 5 replies
  • 0 Likes

Palo Alto's preferred version 10.2 having significant issues

Hi All, 10.1 is going to be EOL in Dec-2024 and if we plan to upgrade on palo alto preferred ver 10.2 then There is a risk that the firewalls may experience significant issues ("popcorn effect"), potentially causing major disruptions to business operations like MFG, RDC, and RND. Anyone has any update or having the same problem? we are waiti...

ssingh by • L0 Member
  • 6858 Views
  • 8 replies
  • 0 Likes

Resolved! GP - Connect with SSL Only

I am running panorama 11.1.3 and using prisma access (Mobile_User_Template). I have read that there is a Connect with SSL Only option but I can not find this. I'm looking in Portal->Agent->App. What am I missing? Here is every setting I have pasted directly from Panorama: Connect MethodPre-logon (Always On)GlobalProtect App Config Re...

THREAT ALERT : high : 169.254.254.238 -> 169.254.255.255 Microsoft Windows NAT Helper DNS Query Denial of Service(31339) alert

Hello Team,We got the below threat alert from the panorama and not able to understand the most of the part , like source and Destination . Both IP looks the outside my network but still its showing the rule: Outbound_Default_URL_IPS . One of my outbound policy with threat prevention rule. Can any one please explain me this .Wondering How can an ...

tiwara by • L3 Networker
  • 13564 Views
  • 7 replies
  • 1 Likes

Resolved! Access limited to tenant

Hi,Is it possible to define user profiles or roles on Cortex XDR so that, for example, on the same tenant: - when a user/admin with role X logs in, he/she can only see Workstations- when a user/admin with role Y logs in, he/she can only see Servers.Is this possible? And if so, what's the procedure for setting it up?best regards,

S.Vilon by • L1 Bithead
  • 1945 Views
  • 2 replies
  • 0 Likes

Traffic log source user different from User-ID log

Hi everyone, Greetings!PA-141011.0.4-h1I have a bit odd issue, the traffic log (ip address) is showing a local firewall account as the source user but when checking the user-mapping (show user ip-user-mapping ip) or User-ID log was mapped to an AD-user. Is it possible for the local firewall account to show as a source user?is it possible that th...

Assistance with URL Filtering

Having some issues getting URL filtering to work as I would expect. Have a valid license, created a URL filter profile blocking some categories. Created and SSL decryption policy as well and applied it to a test users. Games is one of the categories that should be blocked, but for some reason it's allowed and when you go to the log it shows a...

DJ_1924 by • L2 Linker
  • 1078 Views
  • 1 replies
  • 0 Likes

Query regarding counters and debug data-plane pow performance output

Hi Folks, One of our customer is facing CPU utilization of around 50 to 65 percent during the production hours. The firewall model is PA-3220 and the PAN-OS version is 10.1.5. Checked the session utilization, Packet buffer and descriptor all is below 10 percent. When the CPU utilization started to increase the packet rate, throughput and ...

Unable to see IPSEC tunnel IP in trace

Unable to see IPSEC tunnel IP in trace. IPsec tunnels have tunnel interface where the IP is configured. Peer1 - PA Host 1 - behind PA Peer2 - Other vendor Host 2 - behind Peer2 Host 2 trace to HOst1 , can see Ipsec tunnel IPs in trace, when we have Host 1 to host 2 trace, tunnel IPs are missing in trace. Kindly help me know what can ...

  • 24482 Posts
  • 125 Subscriptions
Top Solution Authors
Labels